

A key reaches the product’s API. The API says where to start, and
Authentication shows how an integration uses its key.
How keys work
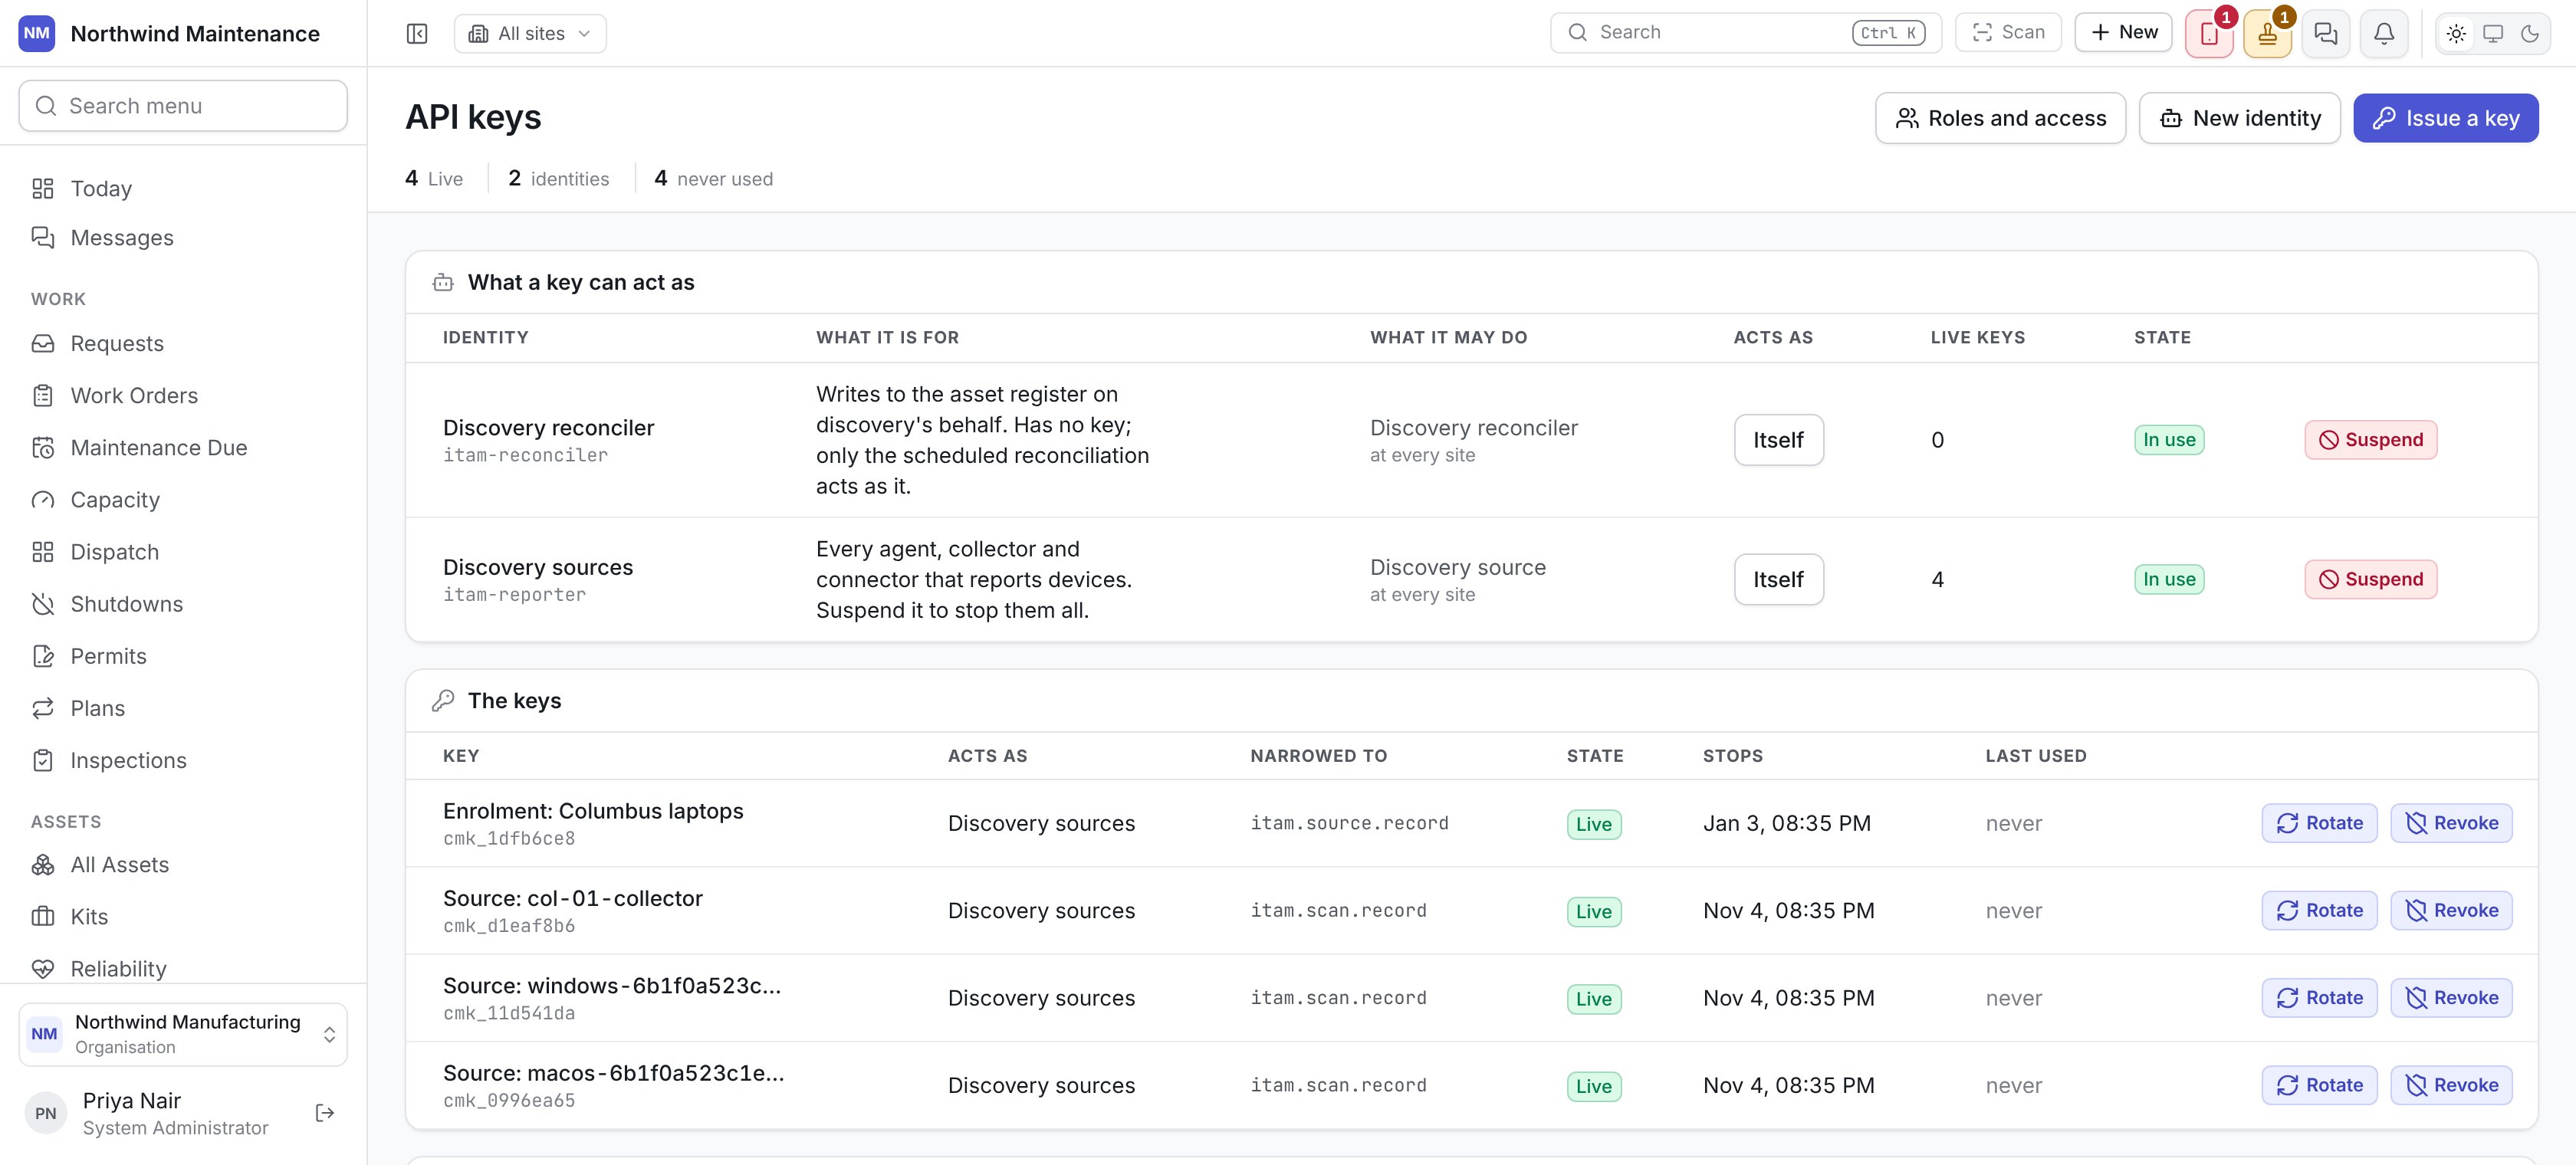
Every key belongs to an identity (a service account), never to a person. The identity holds roles and site access exactly as a person does, and the key can never do more than its identity — it can only be narrowed. That is why the screen shows the identities first: reading a key’s scope without reading the identity behind it is reading half the answer. A key minted from a person’s account would keep working after they left; a key on an identity does not depend on anybody. A key is never sent on ordinary requests. Your integration trades it once for a session token that lasts fifteen minutes, and sends that token on its requests — so the same roles, site limits and audit trail apply to an integration as to somebody using the app. The How a key is used section at the bottom of the screen shows the two requests with this organisation’s address filled in. Reuse a token for its whole fifteen minutes: asking for a new one on every request is refused as a rate limit.The header
If you can read the register but not issue keys, a notice says so: reading which credentials exist is
an access review, while issuing one is closer to creating a user. If you cannot read it at all, the
screen says Not yours to read.
What a key can act as
The machine identities in this organisation.
Identities created by other parts of the product appear here too, such as the ones IT discovery’s
agents and collectors report as.
Acting as itself, or as a person
Switching back to Itself does not end tokens already traded; they keep their fifteen minutes.
Revoke the key to end those.
Creating an identity
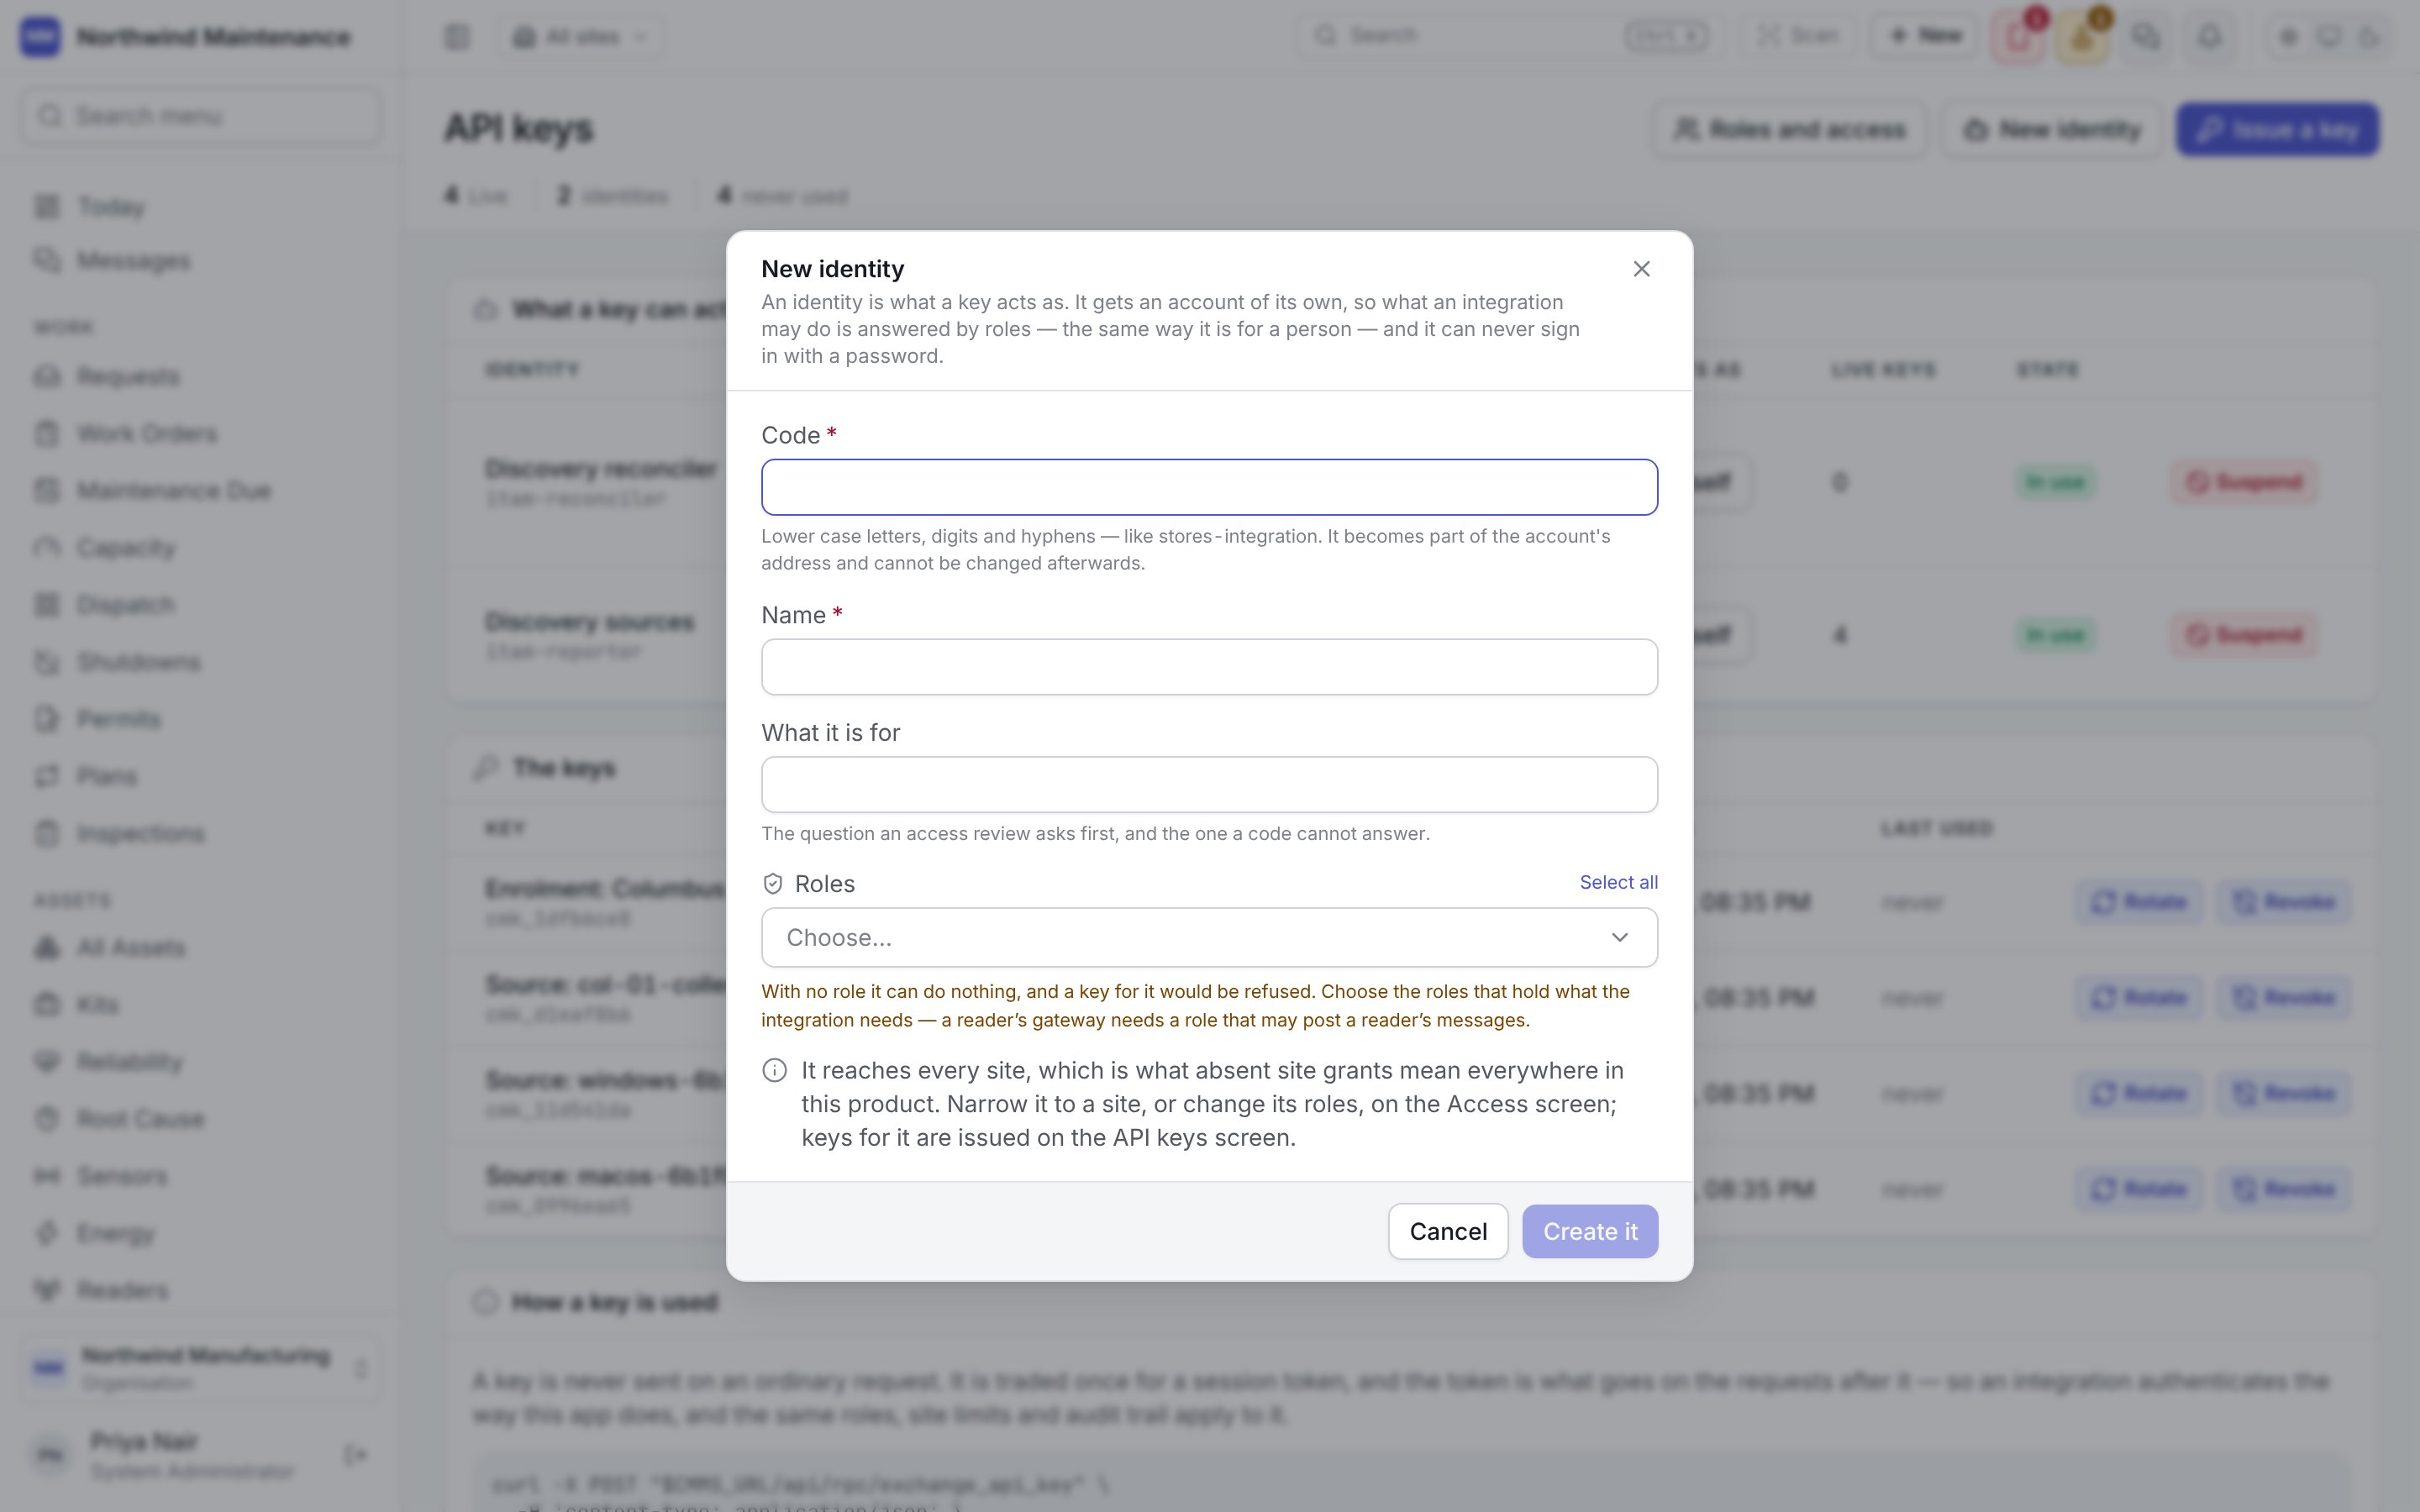
Create it creates the identity. It gets an account of its own that can never sign in with a
password. It starts acting as itself, with the roles you chose, and reaching every site (no site
grants means every site, everywhere in this product). Narrow it to a site, or change its roles, on
Access, then issue it a key here.
The same form opens from Add a service account on Access, and
makes the same thing: an identity made on either screen is offered under Acts as straight away.
The keys
Issuing a key
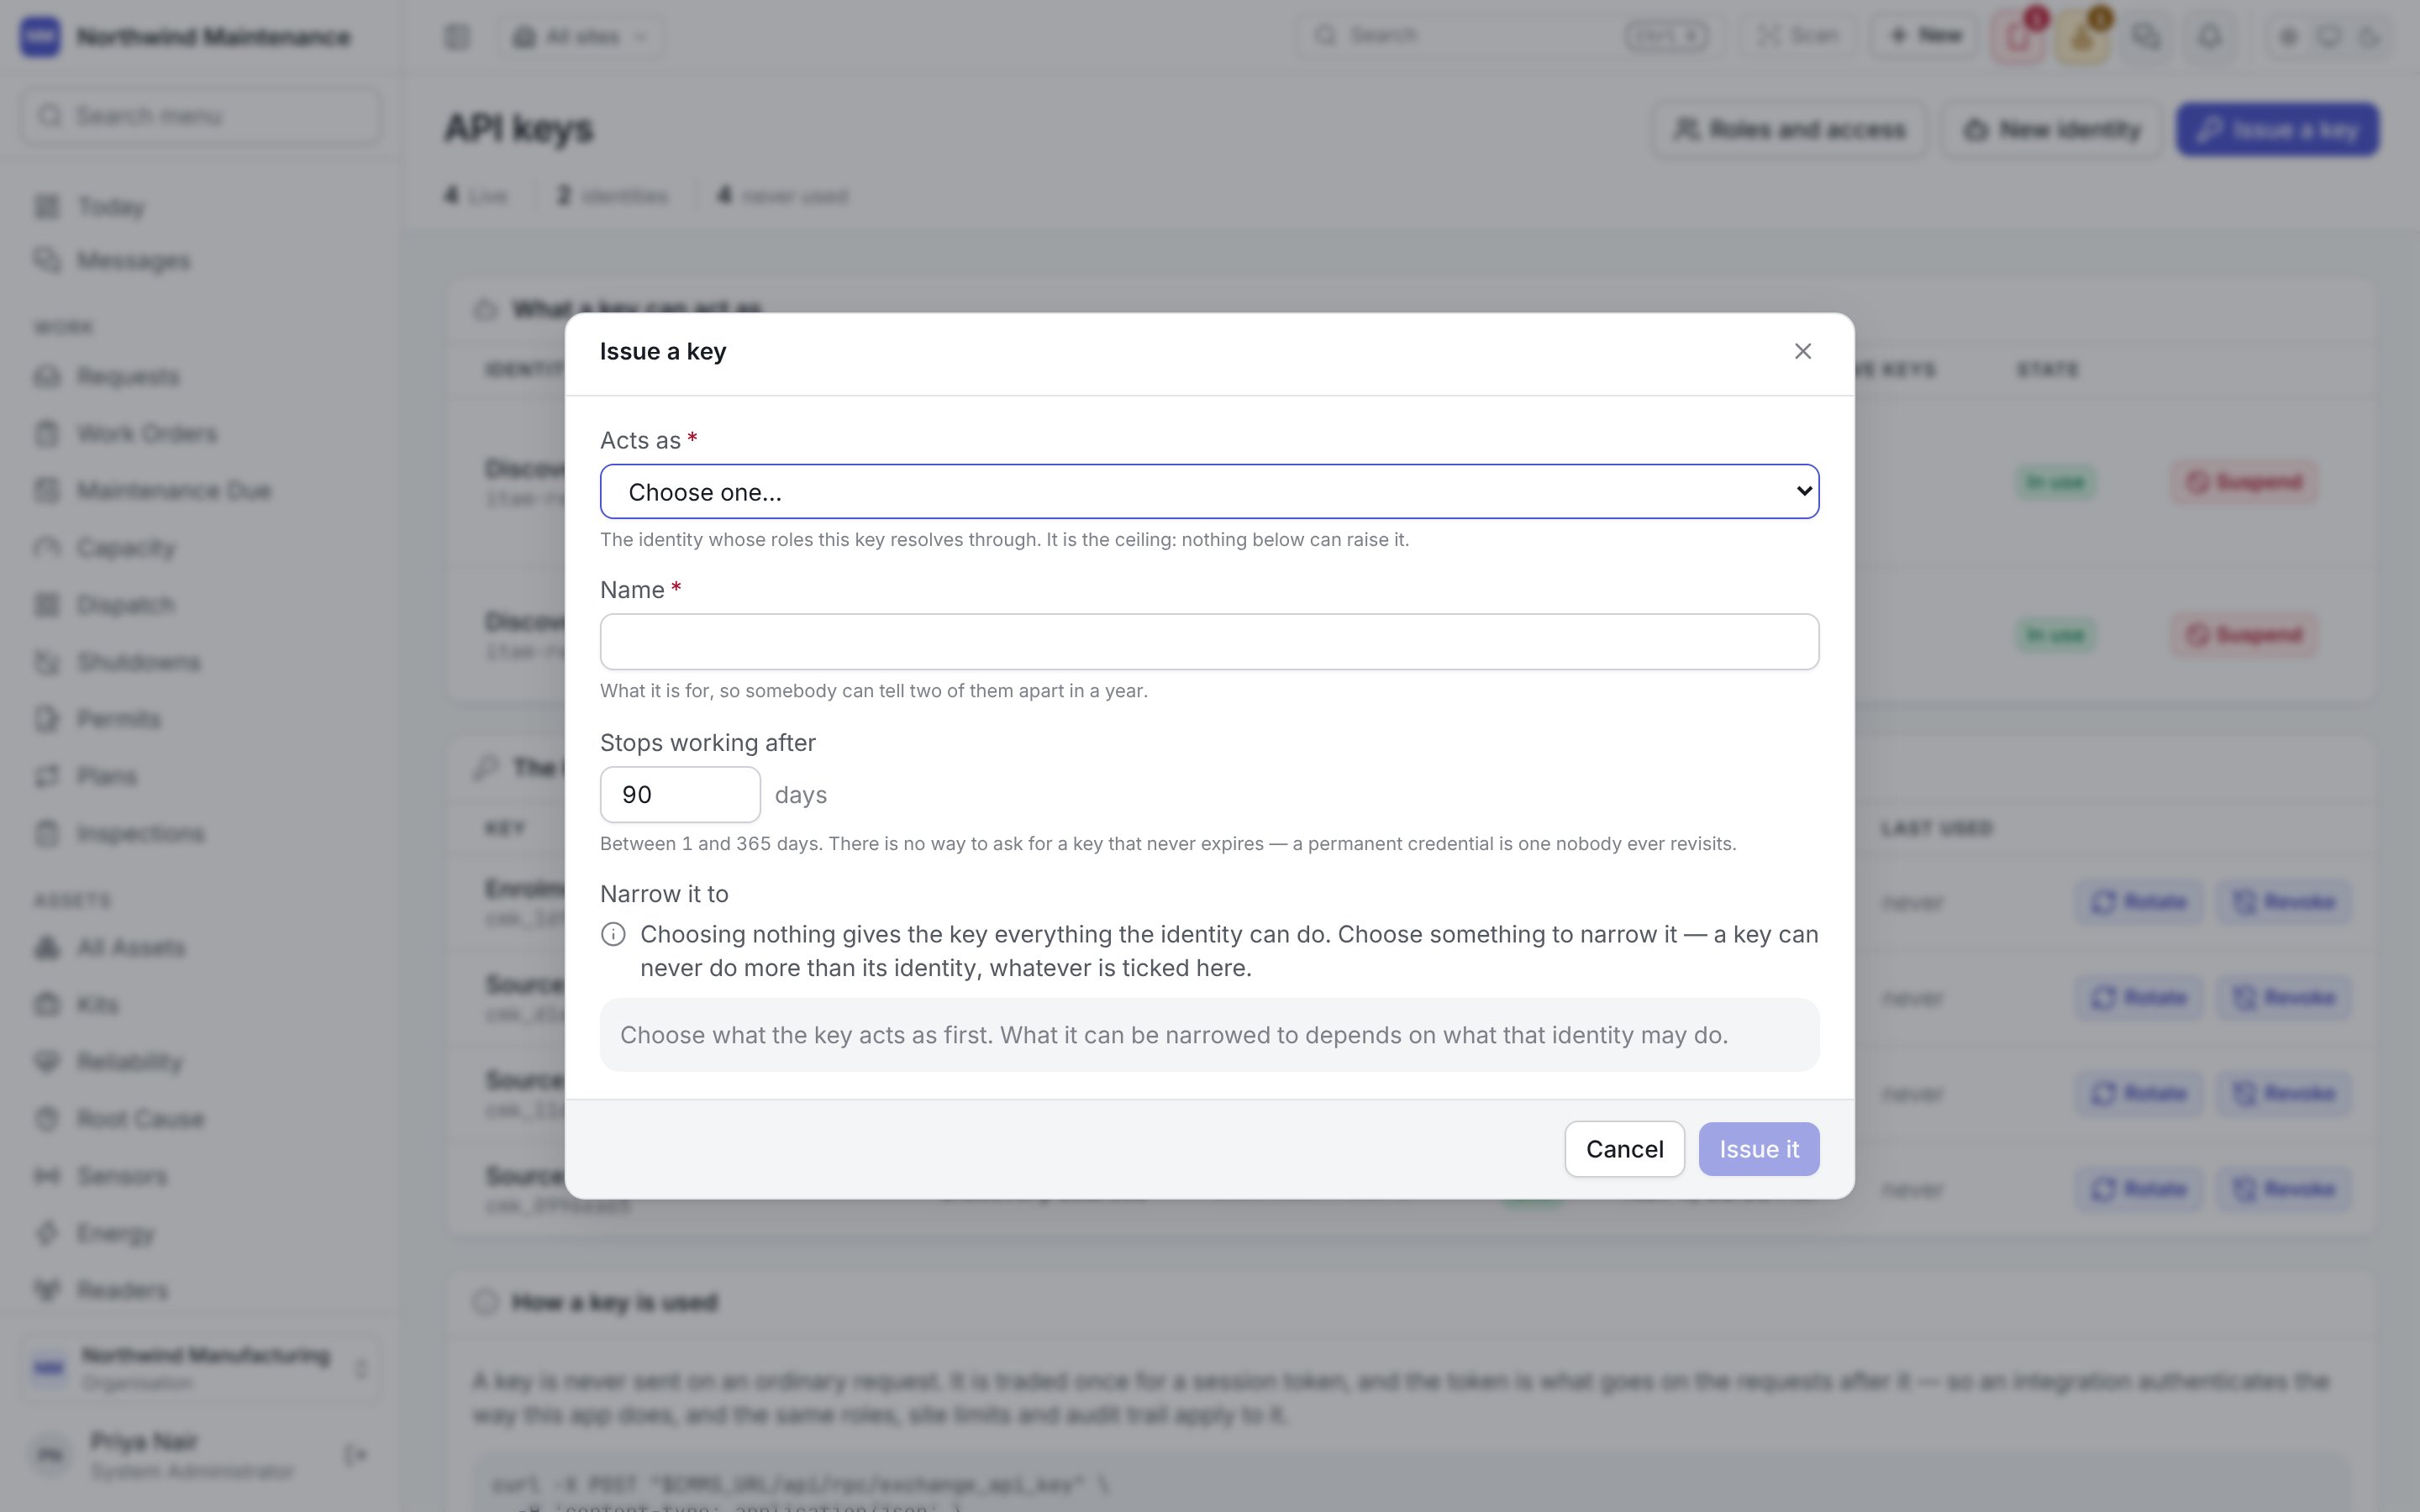
Issue it creates the key and shows it once.
Rotating a key
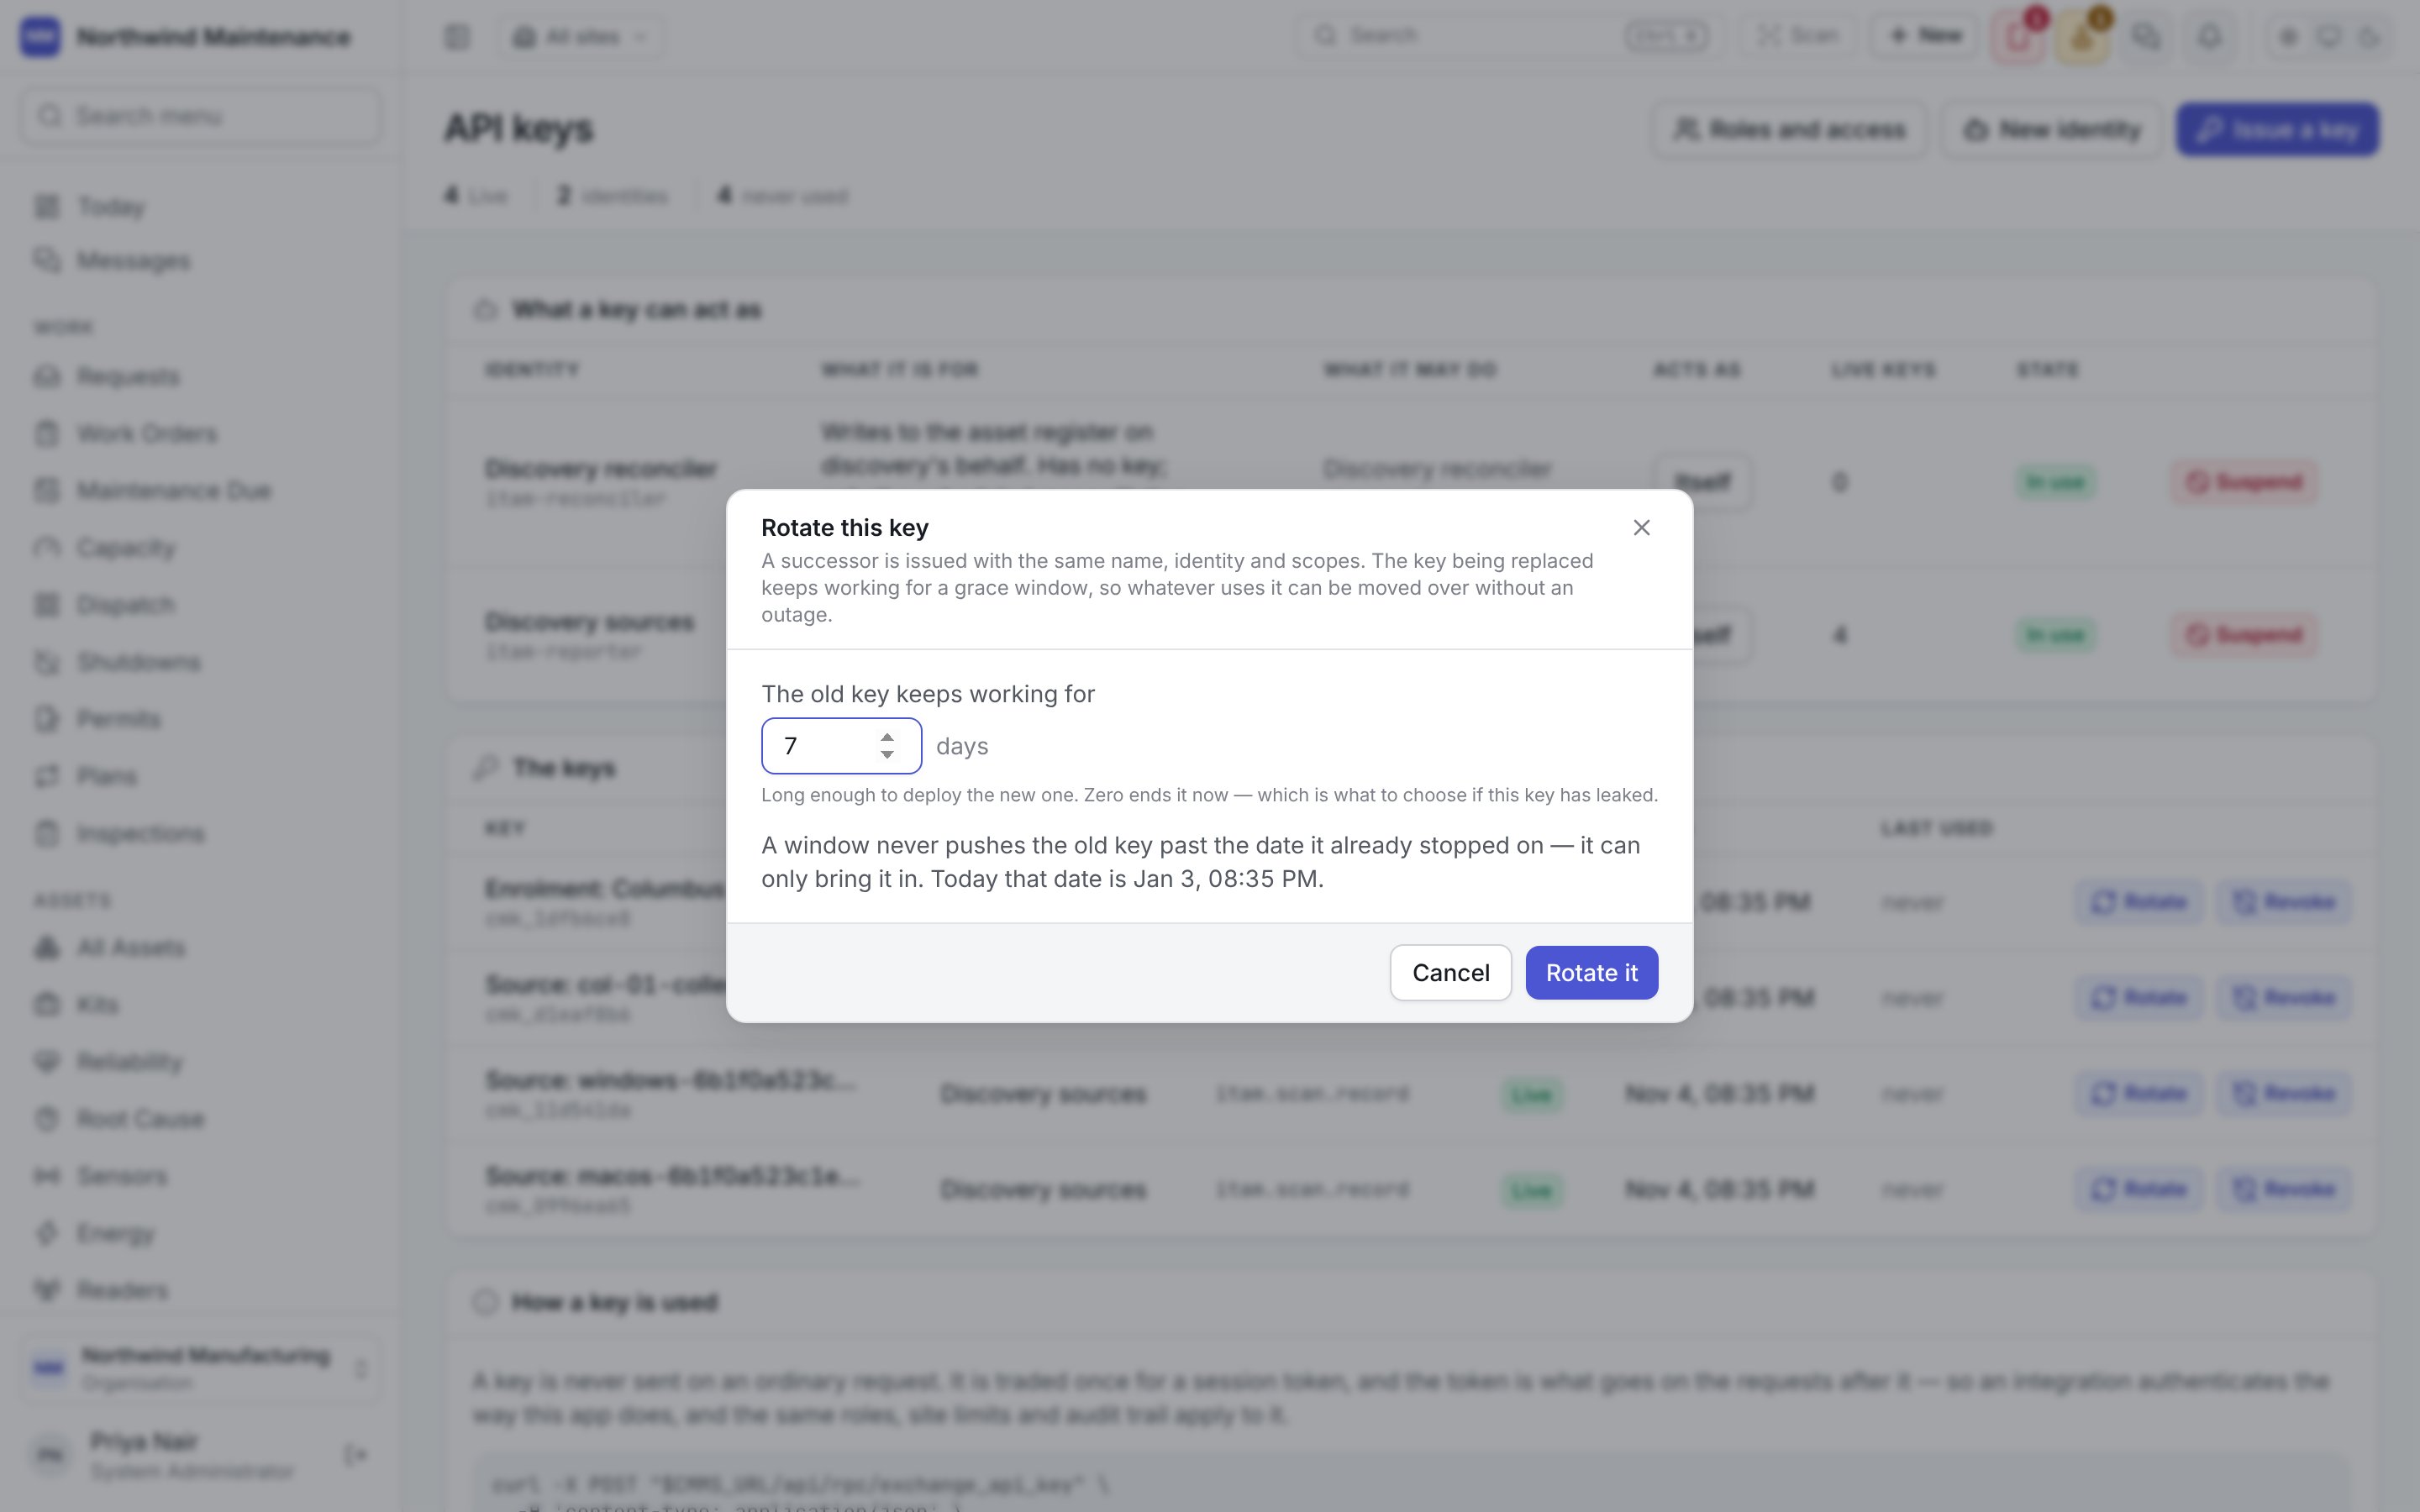
There is no way to widen a key. Rotation carries the scope forward, and a wider key is a new key.
Revoking a key
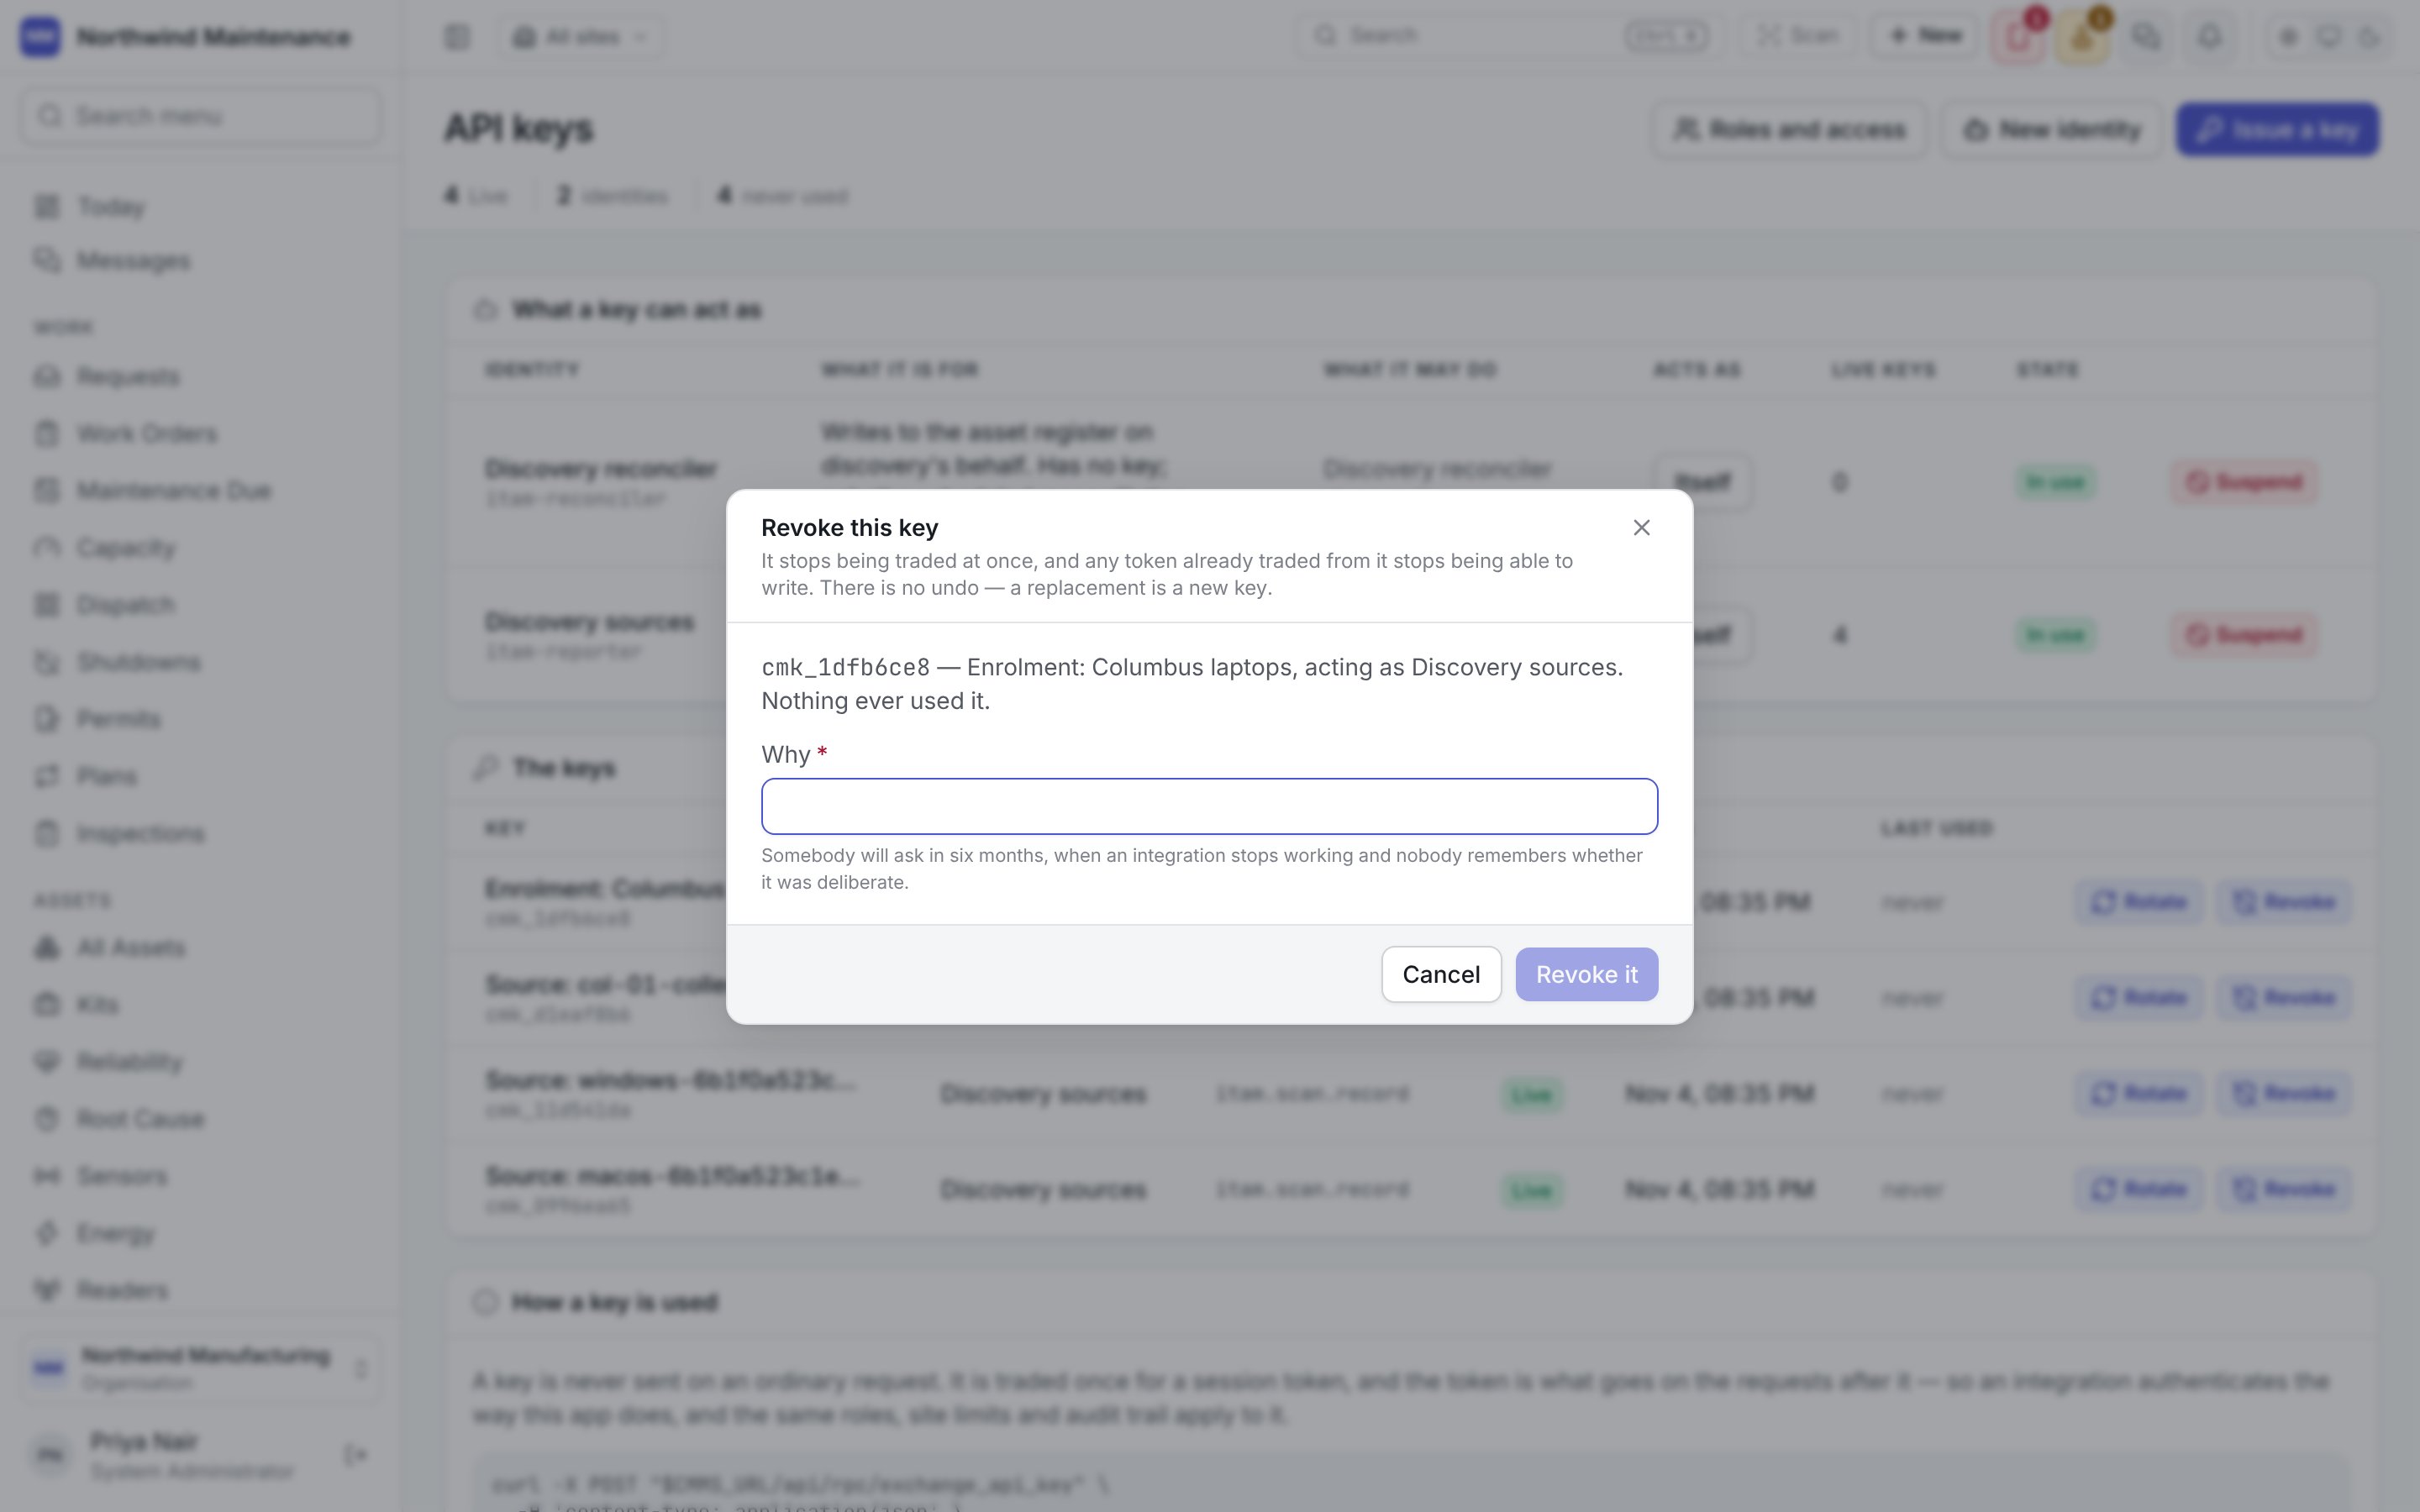
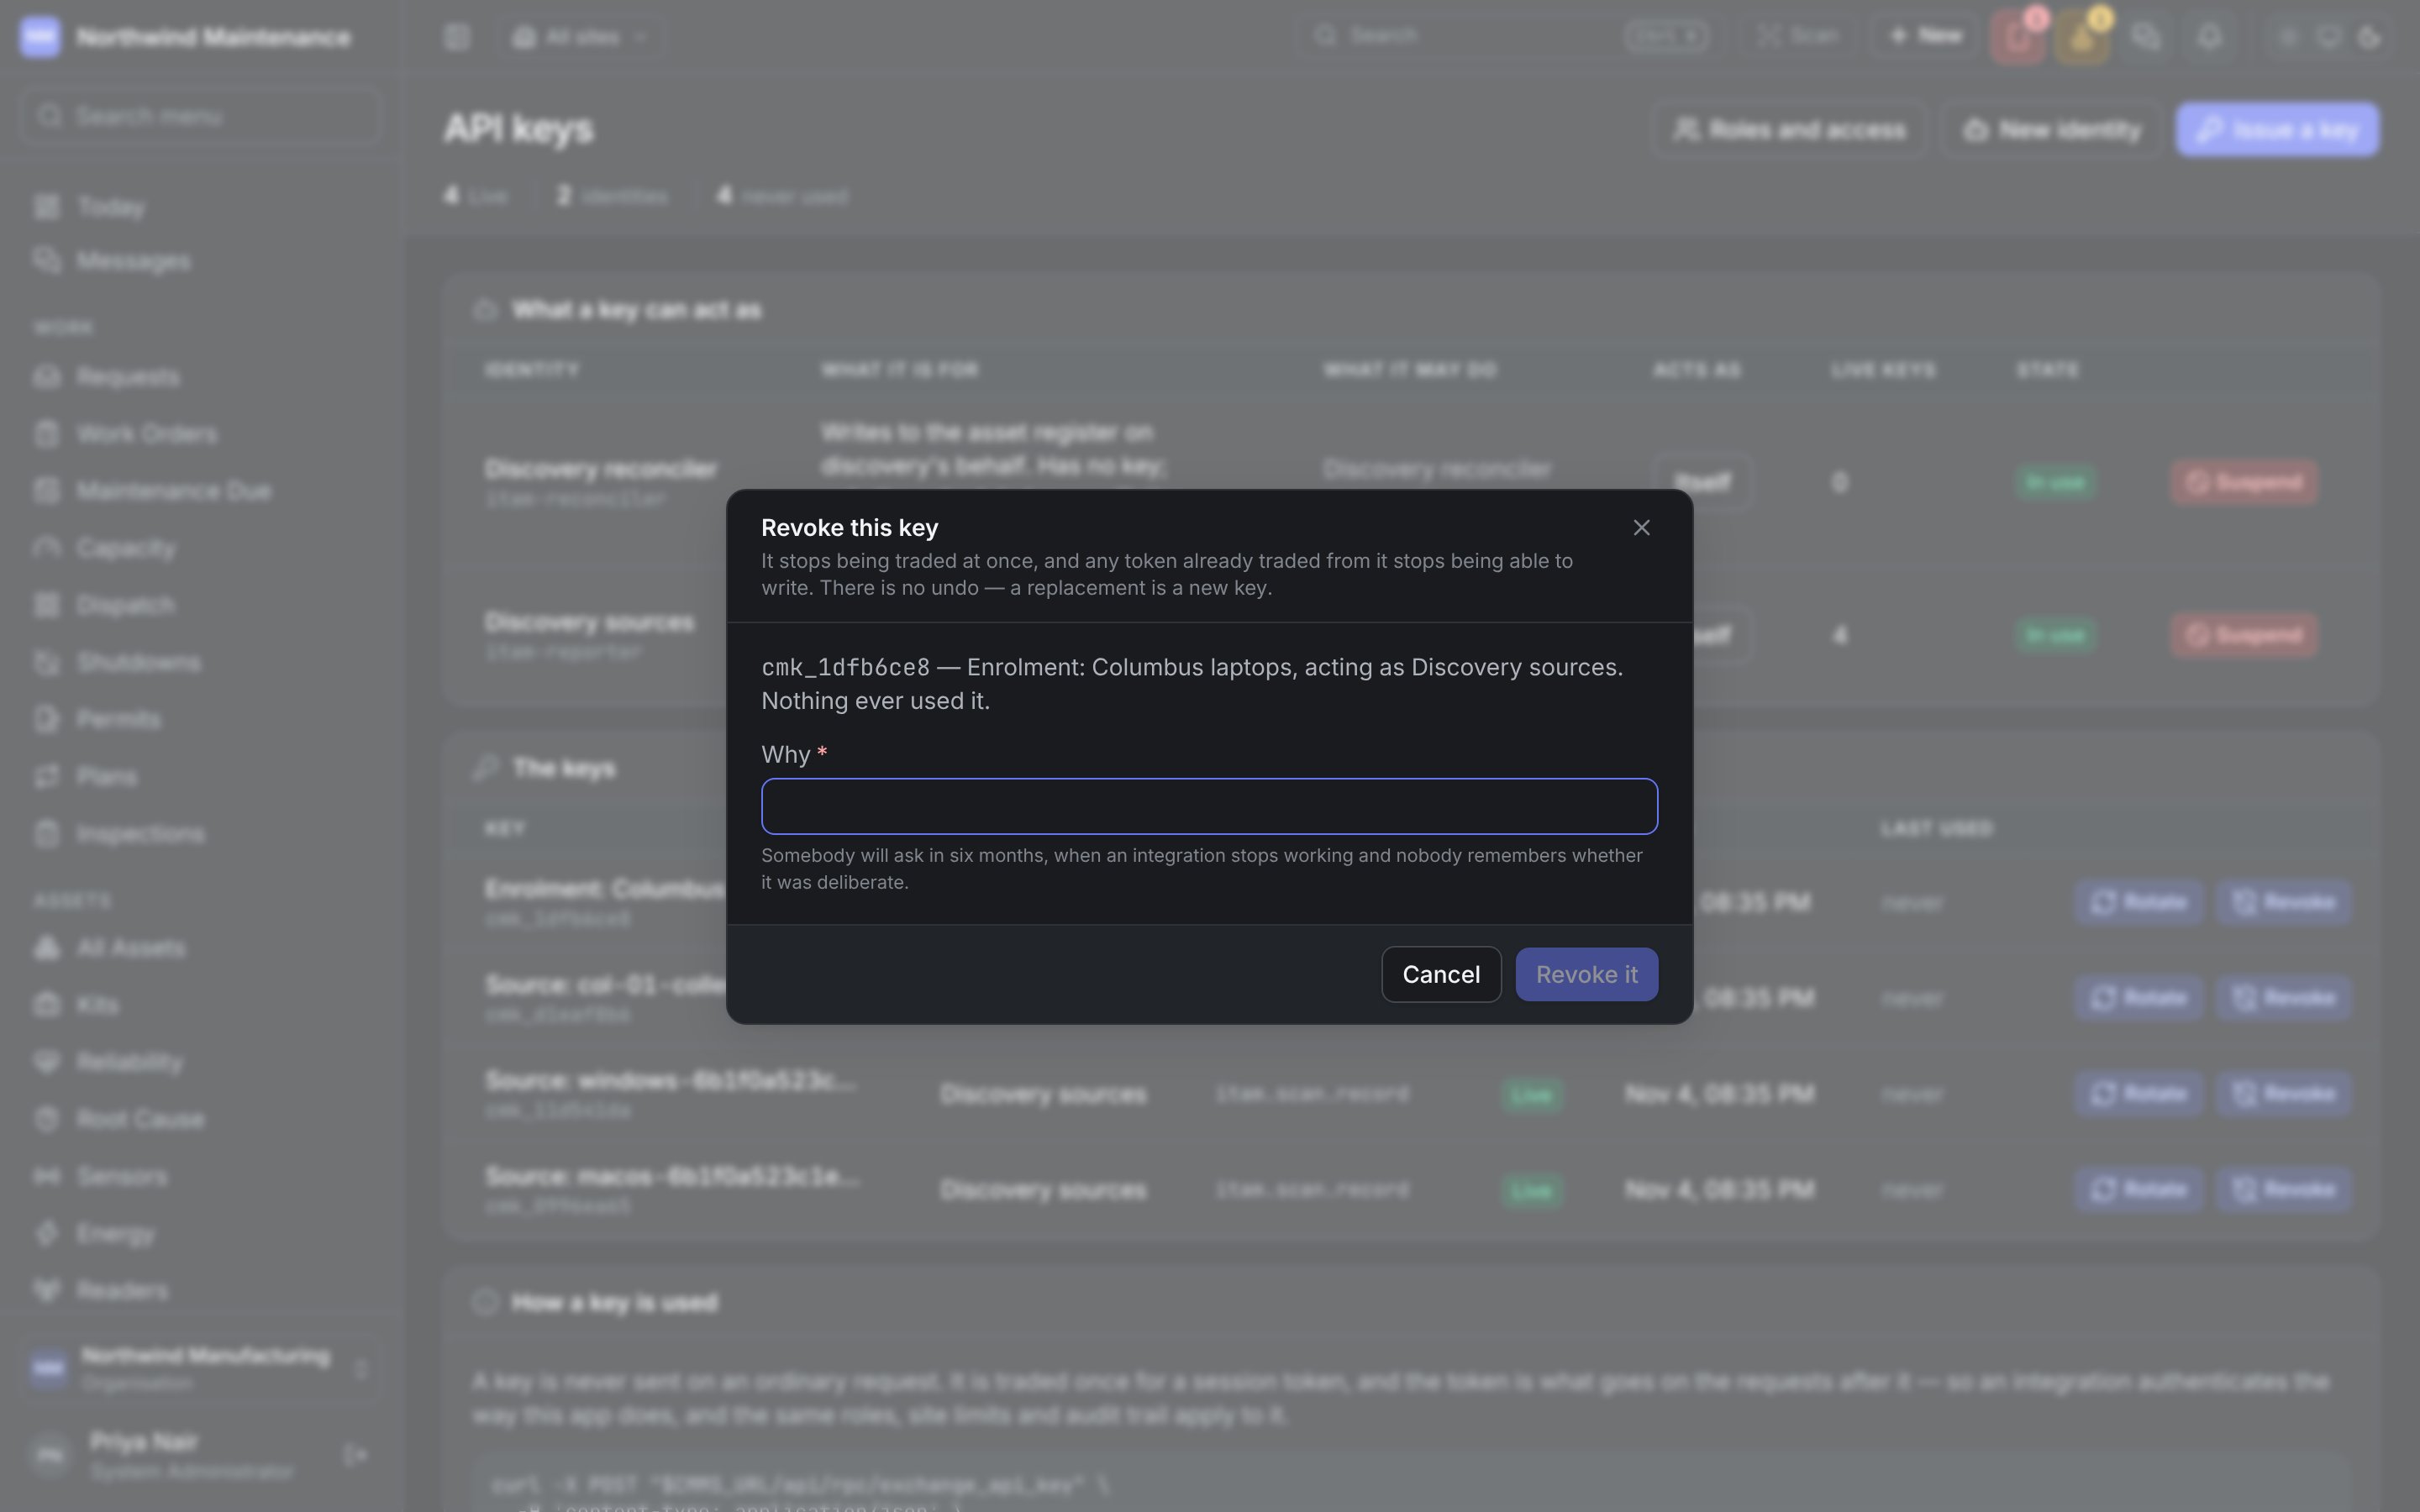
Revoke it stops the key being traded for a token at once, and stops any token already traded from
writing anything; a read can finish out the token’s last few minutes. There is no undo — a
replacement is a new key.
Finding the call behind a screen
Whoever builds an integration usually needs to know which call a screen makes — which call adds an asset, for instance. Turn on Developer mode in your profile and every screen gains an API button (Show the API behind this screen). It opens The API behind this screen, listing the Functions it calls and the Read models it reads, each described in the same words as the API reference, for the version your organisation is running. For a call that changes something, What to send writes an example request carrying every field the call accepts, required ones first, each with a placeholder of the right kind — a number, a yes or no, a text, or the identifier of a record together with where that identifier comes from. Copy the request copies it. Hide the rest trims the request back to the fields a create cannot proceed without, listing the others under And the ones it can do without. Developer mode is only offered to people whose role lets them view integrations, and it changes nothing about what they may read or write.Who can manage this
None of these is on the Maintenance Administrator’s default pattern: a credential that can reach the
whole API is not maintenance configuration. See roles.
The API
What a key can reach, and where to start building with it.
Security events
Issuing a collector key that can follow the audit trail and nothing else.