

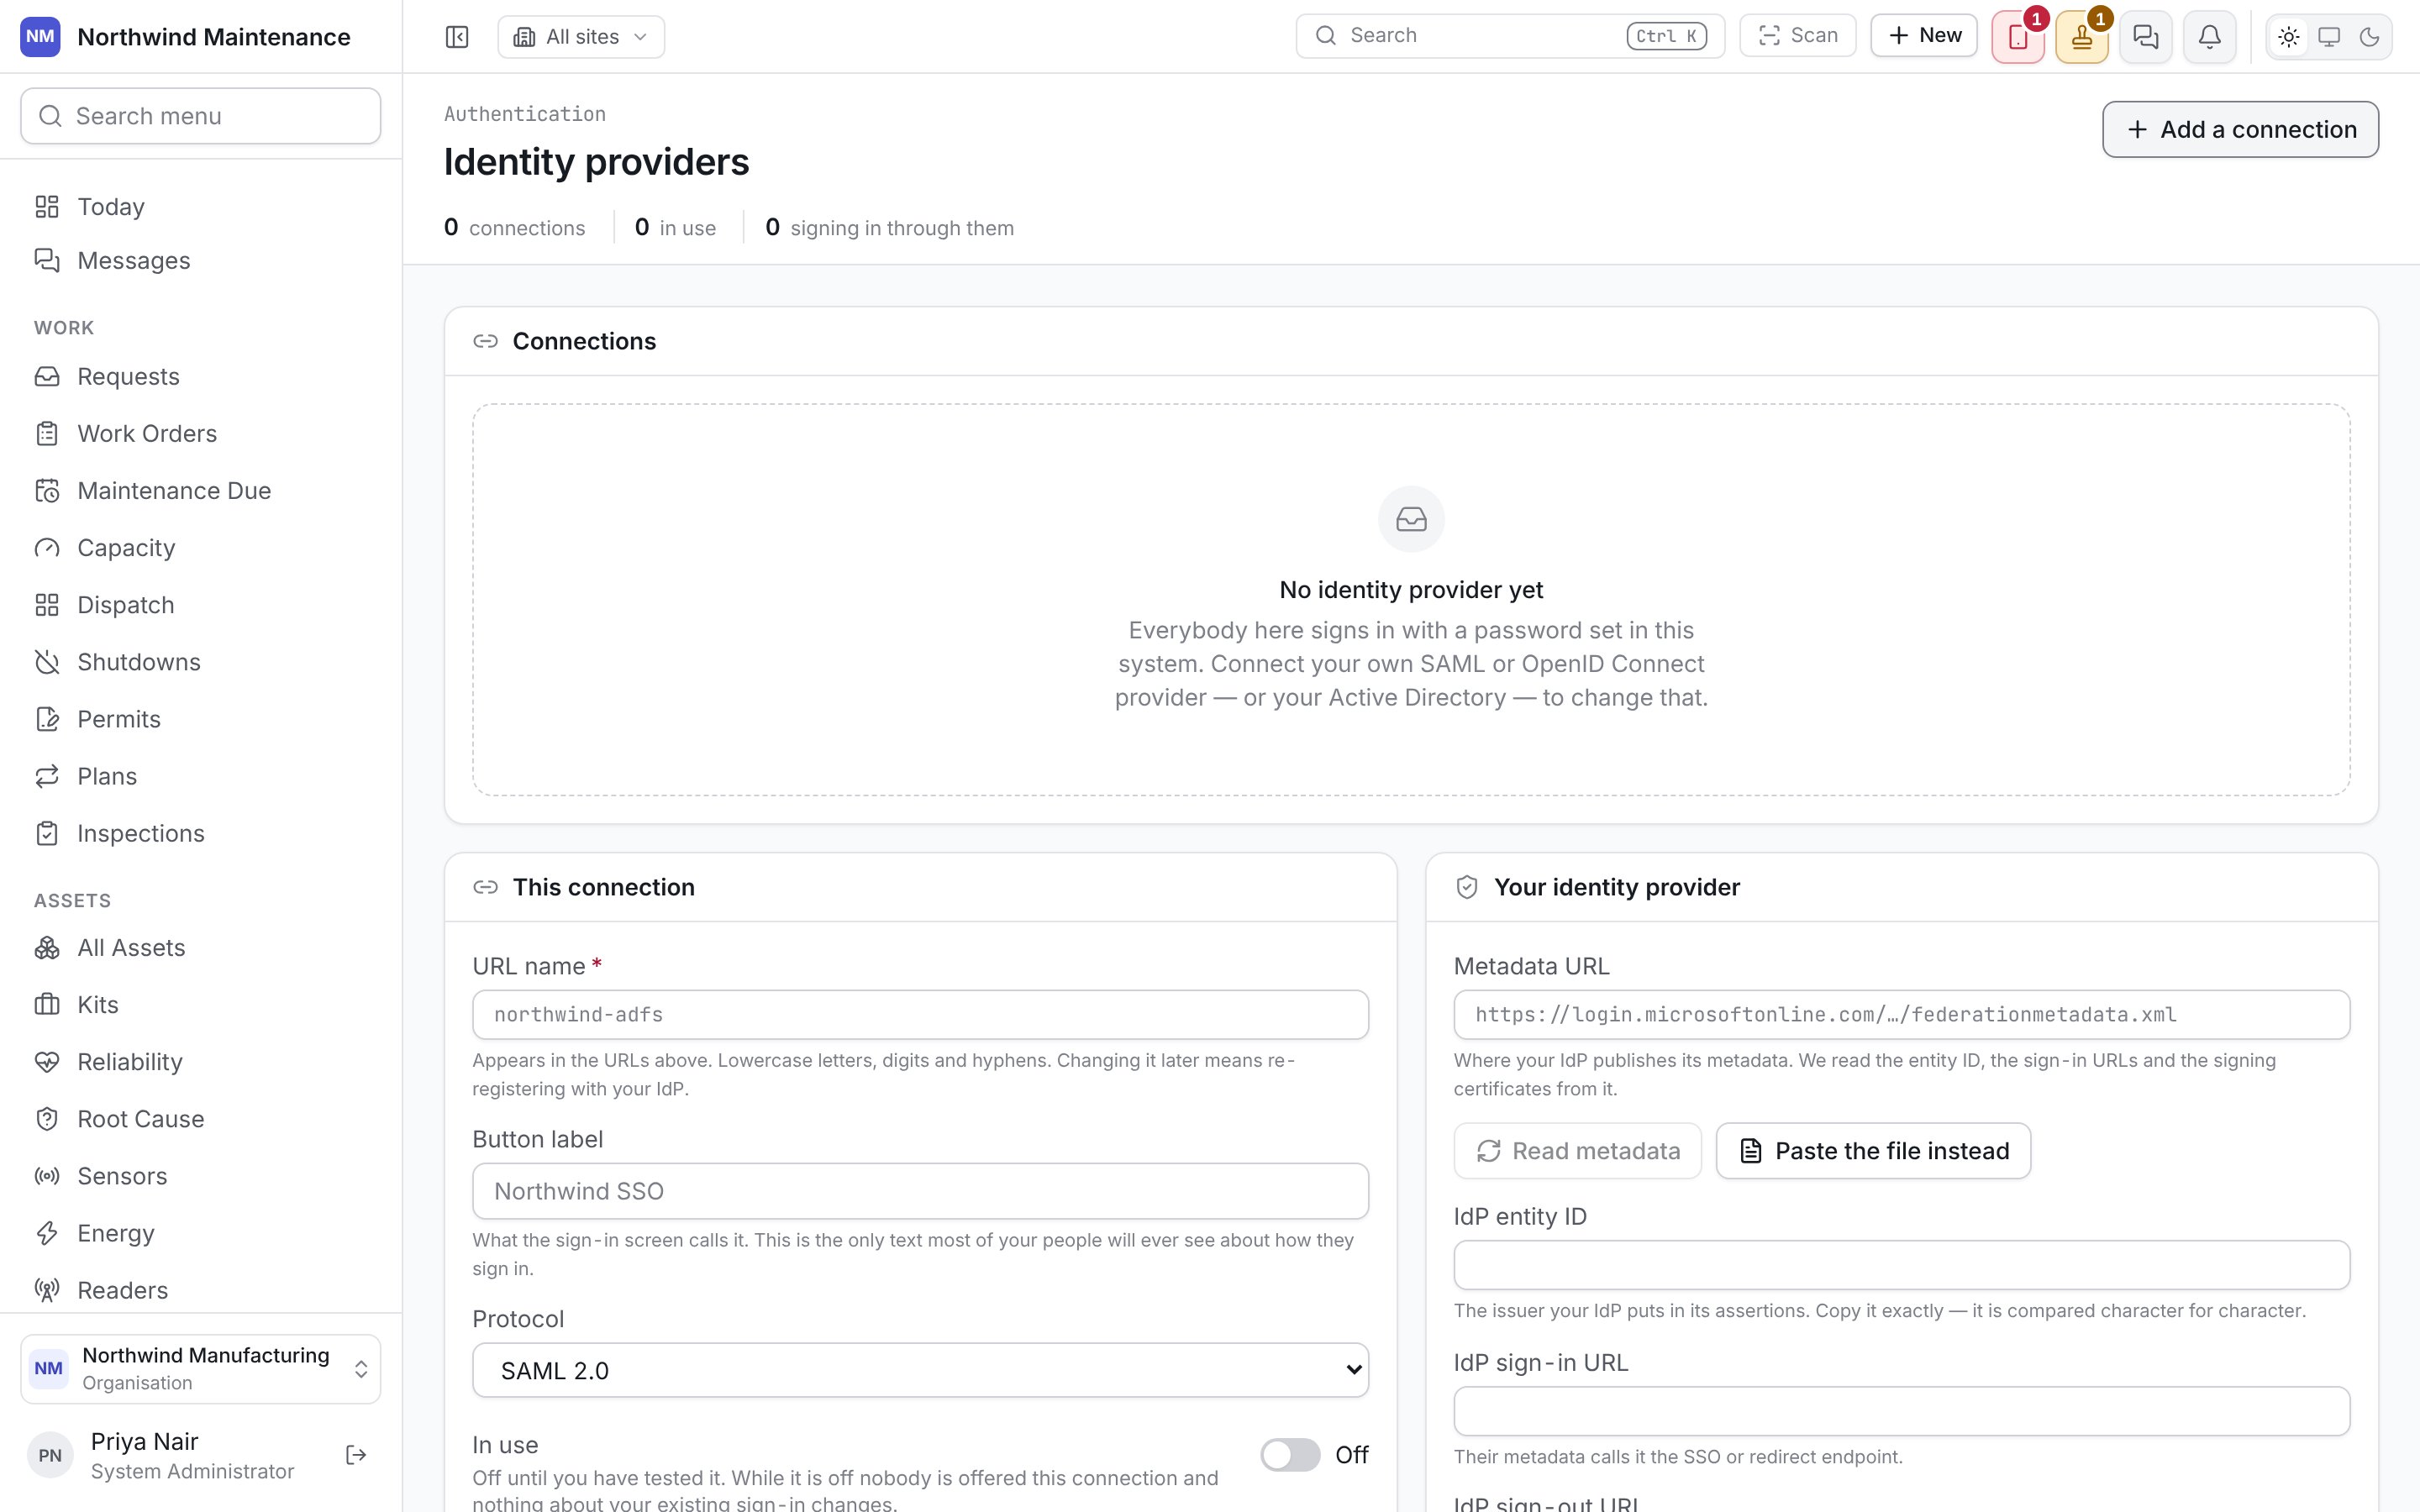
The screen at a glance
The header carries three figures:
Add a connection opens an empty connection panel below the list. You see it only if you can
configure sign-in (see who can use this). Everybody else sees a notice saying
they can read the connections but not change them.
The connections list
Click a row to open that connection’s panel underneath.
With no connections, the list says No identity provider yet: everybody signs in with a password
set in this system.
Choosing a protocol
The protocol is chosen when the connection is created and cannot be changed afterwards. To move
from one protocol to another, add a second connection.
Nothing is switched on by saving it. A connection is saved with In use off. Configuring
SAML or OpenID Connect is a two-way exchange — values from your identity provider into this form,
and values from this form back into theirs — so nobody is offered the connection until you have
finished both halves, tested it and switched it on. Saving never signs anybody out; the banner
after a save says so.
The connection panel
The panel is a set of sections. Which ones appear depends on the protocol and on whether the connection has been saved yet.
At the bottom, Create connection (or Save connection for a saved one) saves every section of
the form at once. Close discards unsaved changes. Delete connection removes a saved one;
if accounts sign in through it, a line under the buttons says how many, because accounts created
through a connection have no password and deleting it removes their only way in.
The last refusal
When your identity provider or directory last refused somebody, the panel opens with a red banner: The last sign-in through this connection was refused: followed by the reason and when. The commonest causes are an expired signing certificate, a clock difference, or a value copied with a character missing. This banner is the answer to “is it us or is it them” while you have your identity provider team on the phone.This connection
Setting up SAML 2.0
What to give your identity provider
As soon as the URL name is filled in, a section at the top of the panel shows the values your identity provider needs when you register this application with it. Each has a copy button.Your identity provider
When a metadata read changes a value the connection already had saved, the hint under that field
says Changed by the metadata. This connection had … so you can see what moved before you save.
A metadata read can also show two warnings:
Certificates found in the metadata
Under the form, a metadata read lists Signing certificates in this metadata, each with its SHA-256 fingerprint, subject and expiry, and a state:
Ticking is not trusting: ticked certificates are trusted only when you save. Check each fingerprint
against what your identity provider shows before you do. Below the list, any certificate still in
use here that the identity provider no longer publishes is offered with a Retire button. It is
not retired automatically, because identity providers usually stop publishing a certificate a little
before they stop signing with it.
If the metadata publishes no signing certificate at all, the screen says so. Paste one in the
Signing certificates section once the connection is saved, or nobody can sign in through it.
Setting up OpenID Connect
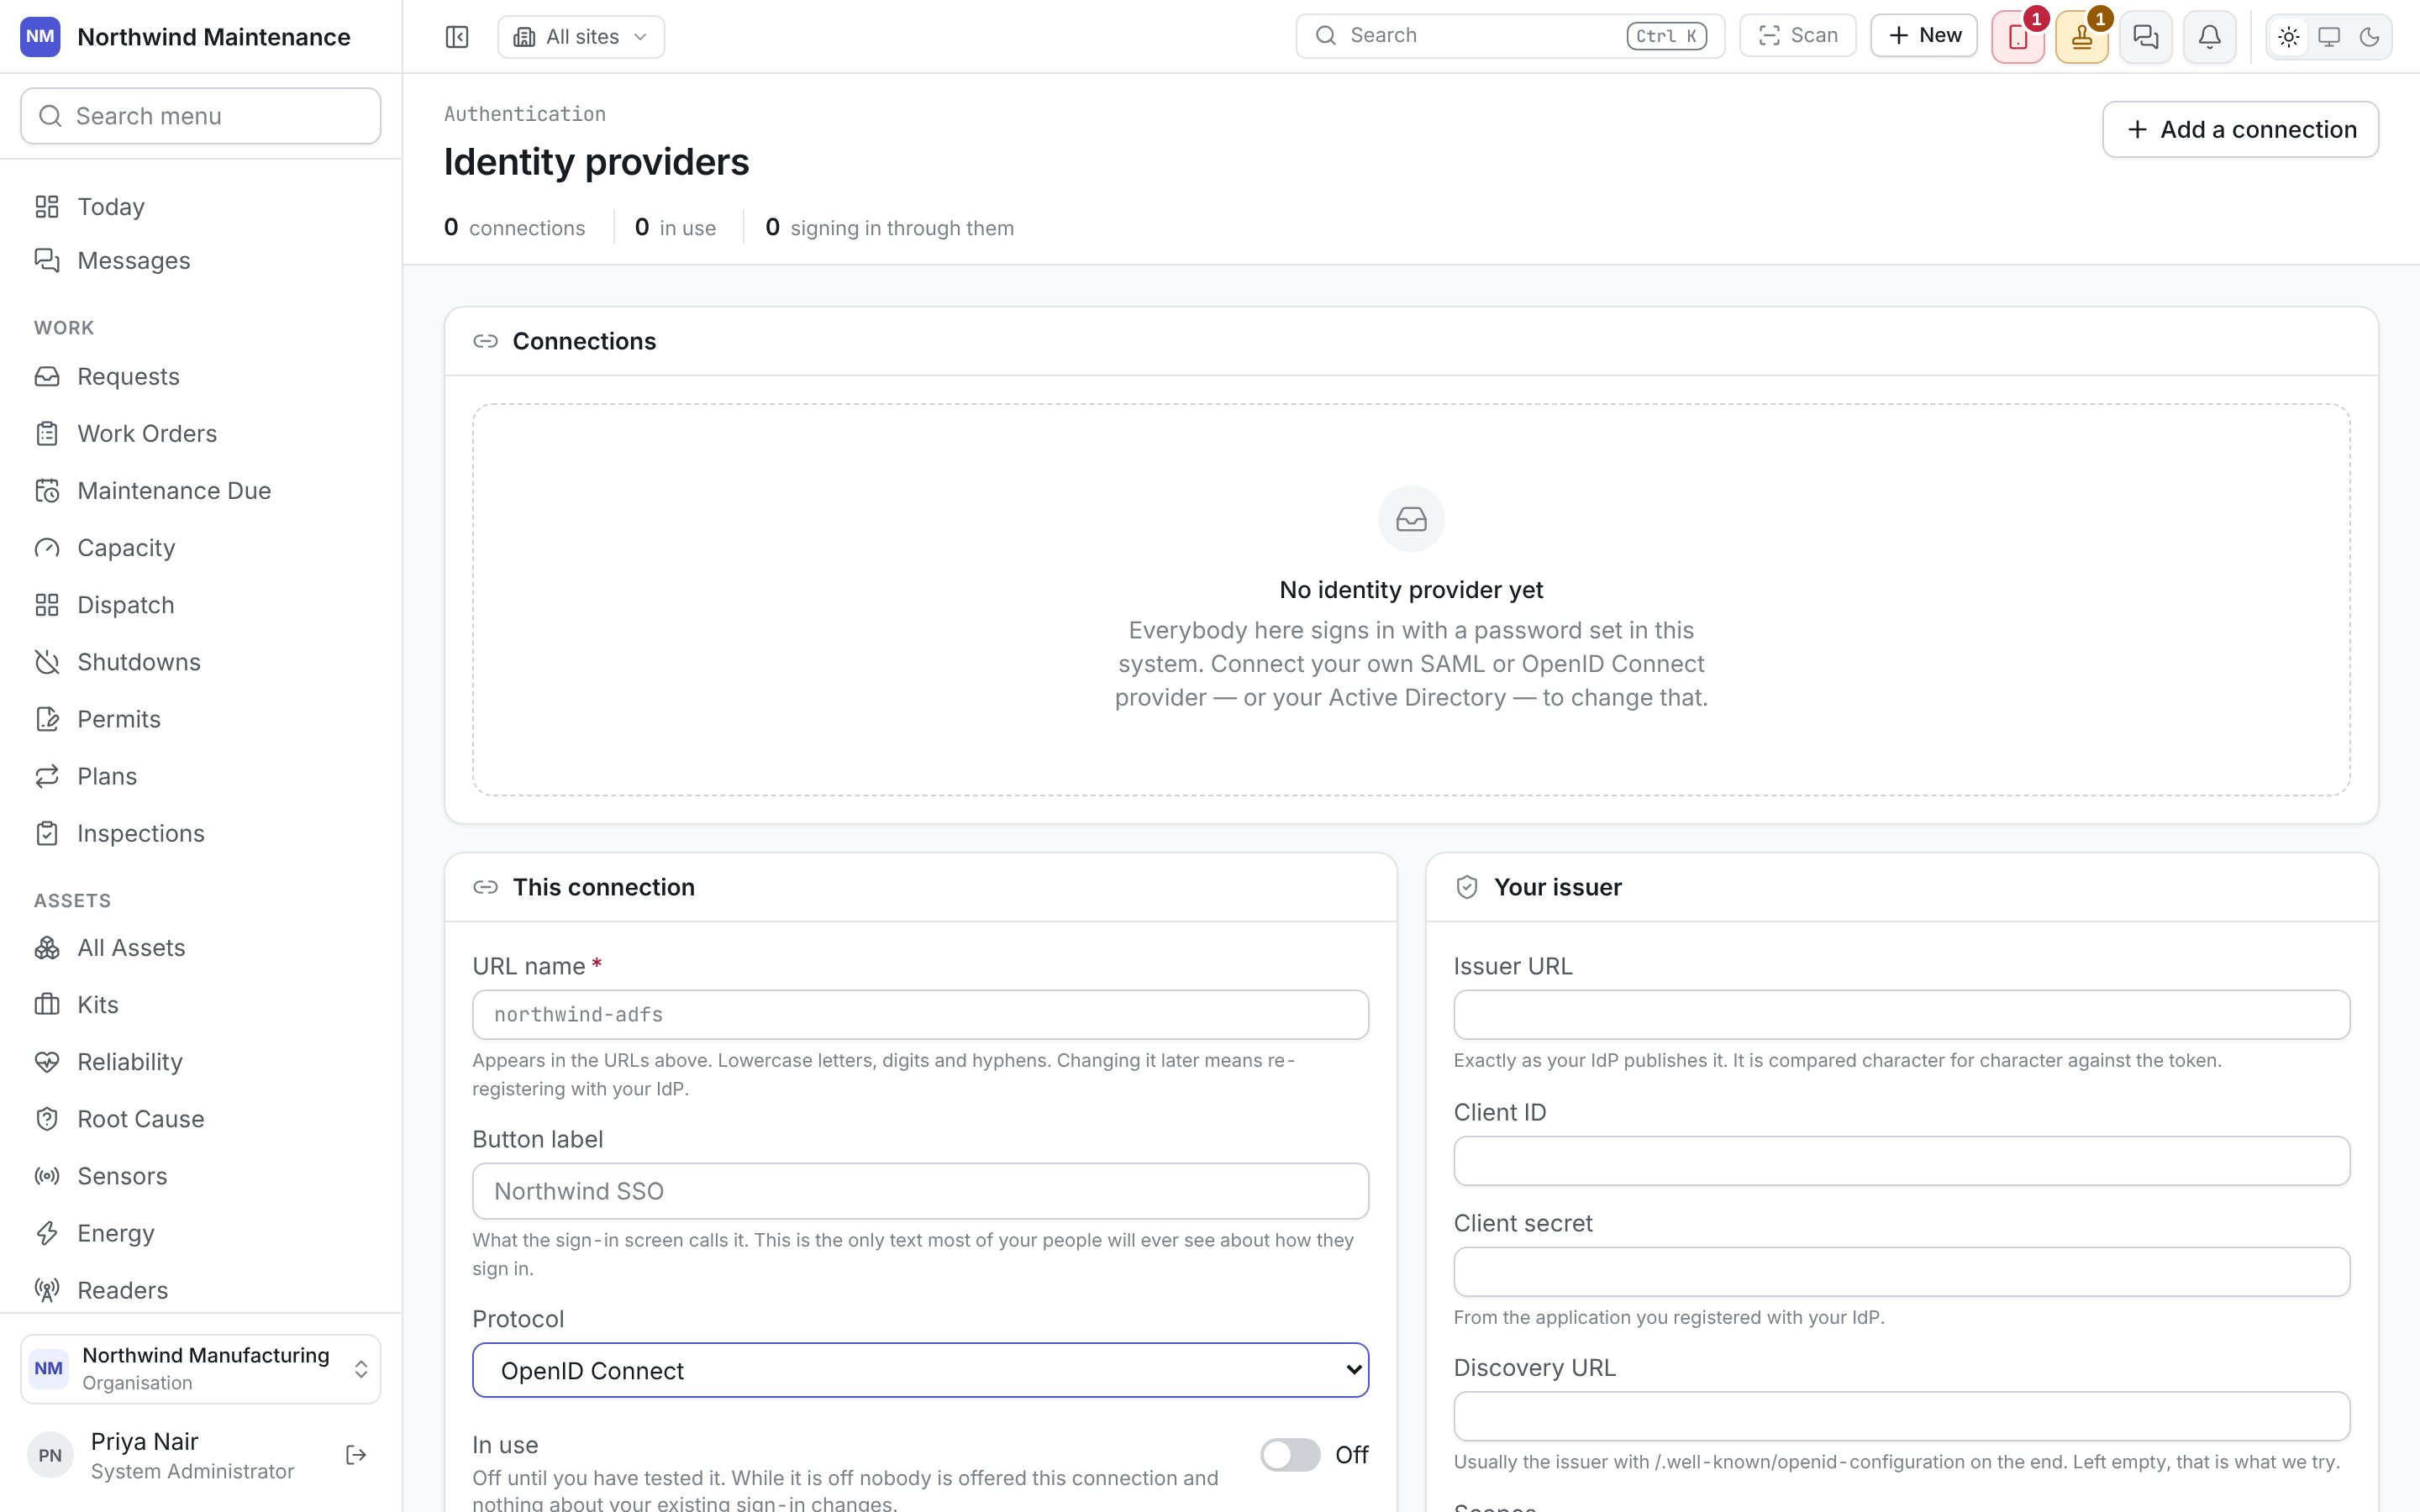
Your issuer
Setting up LDAP / Active Directory
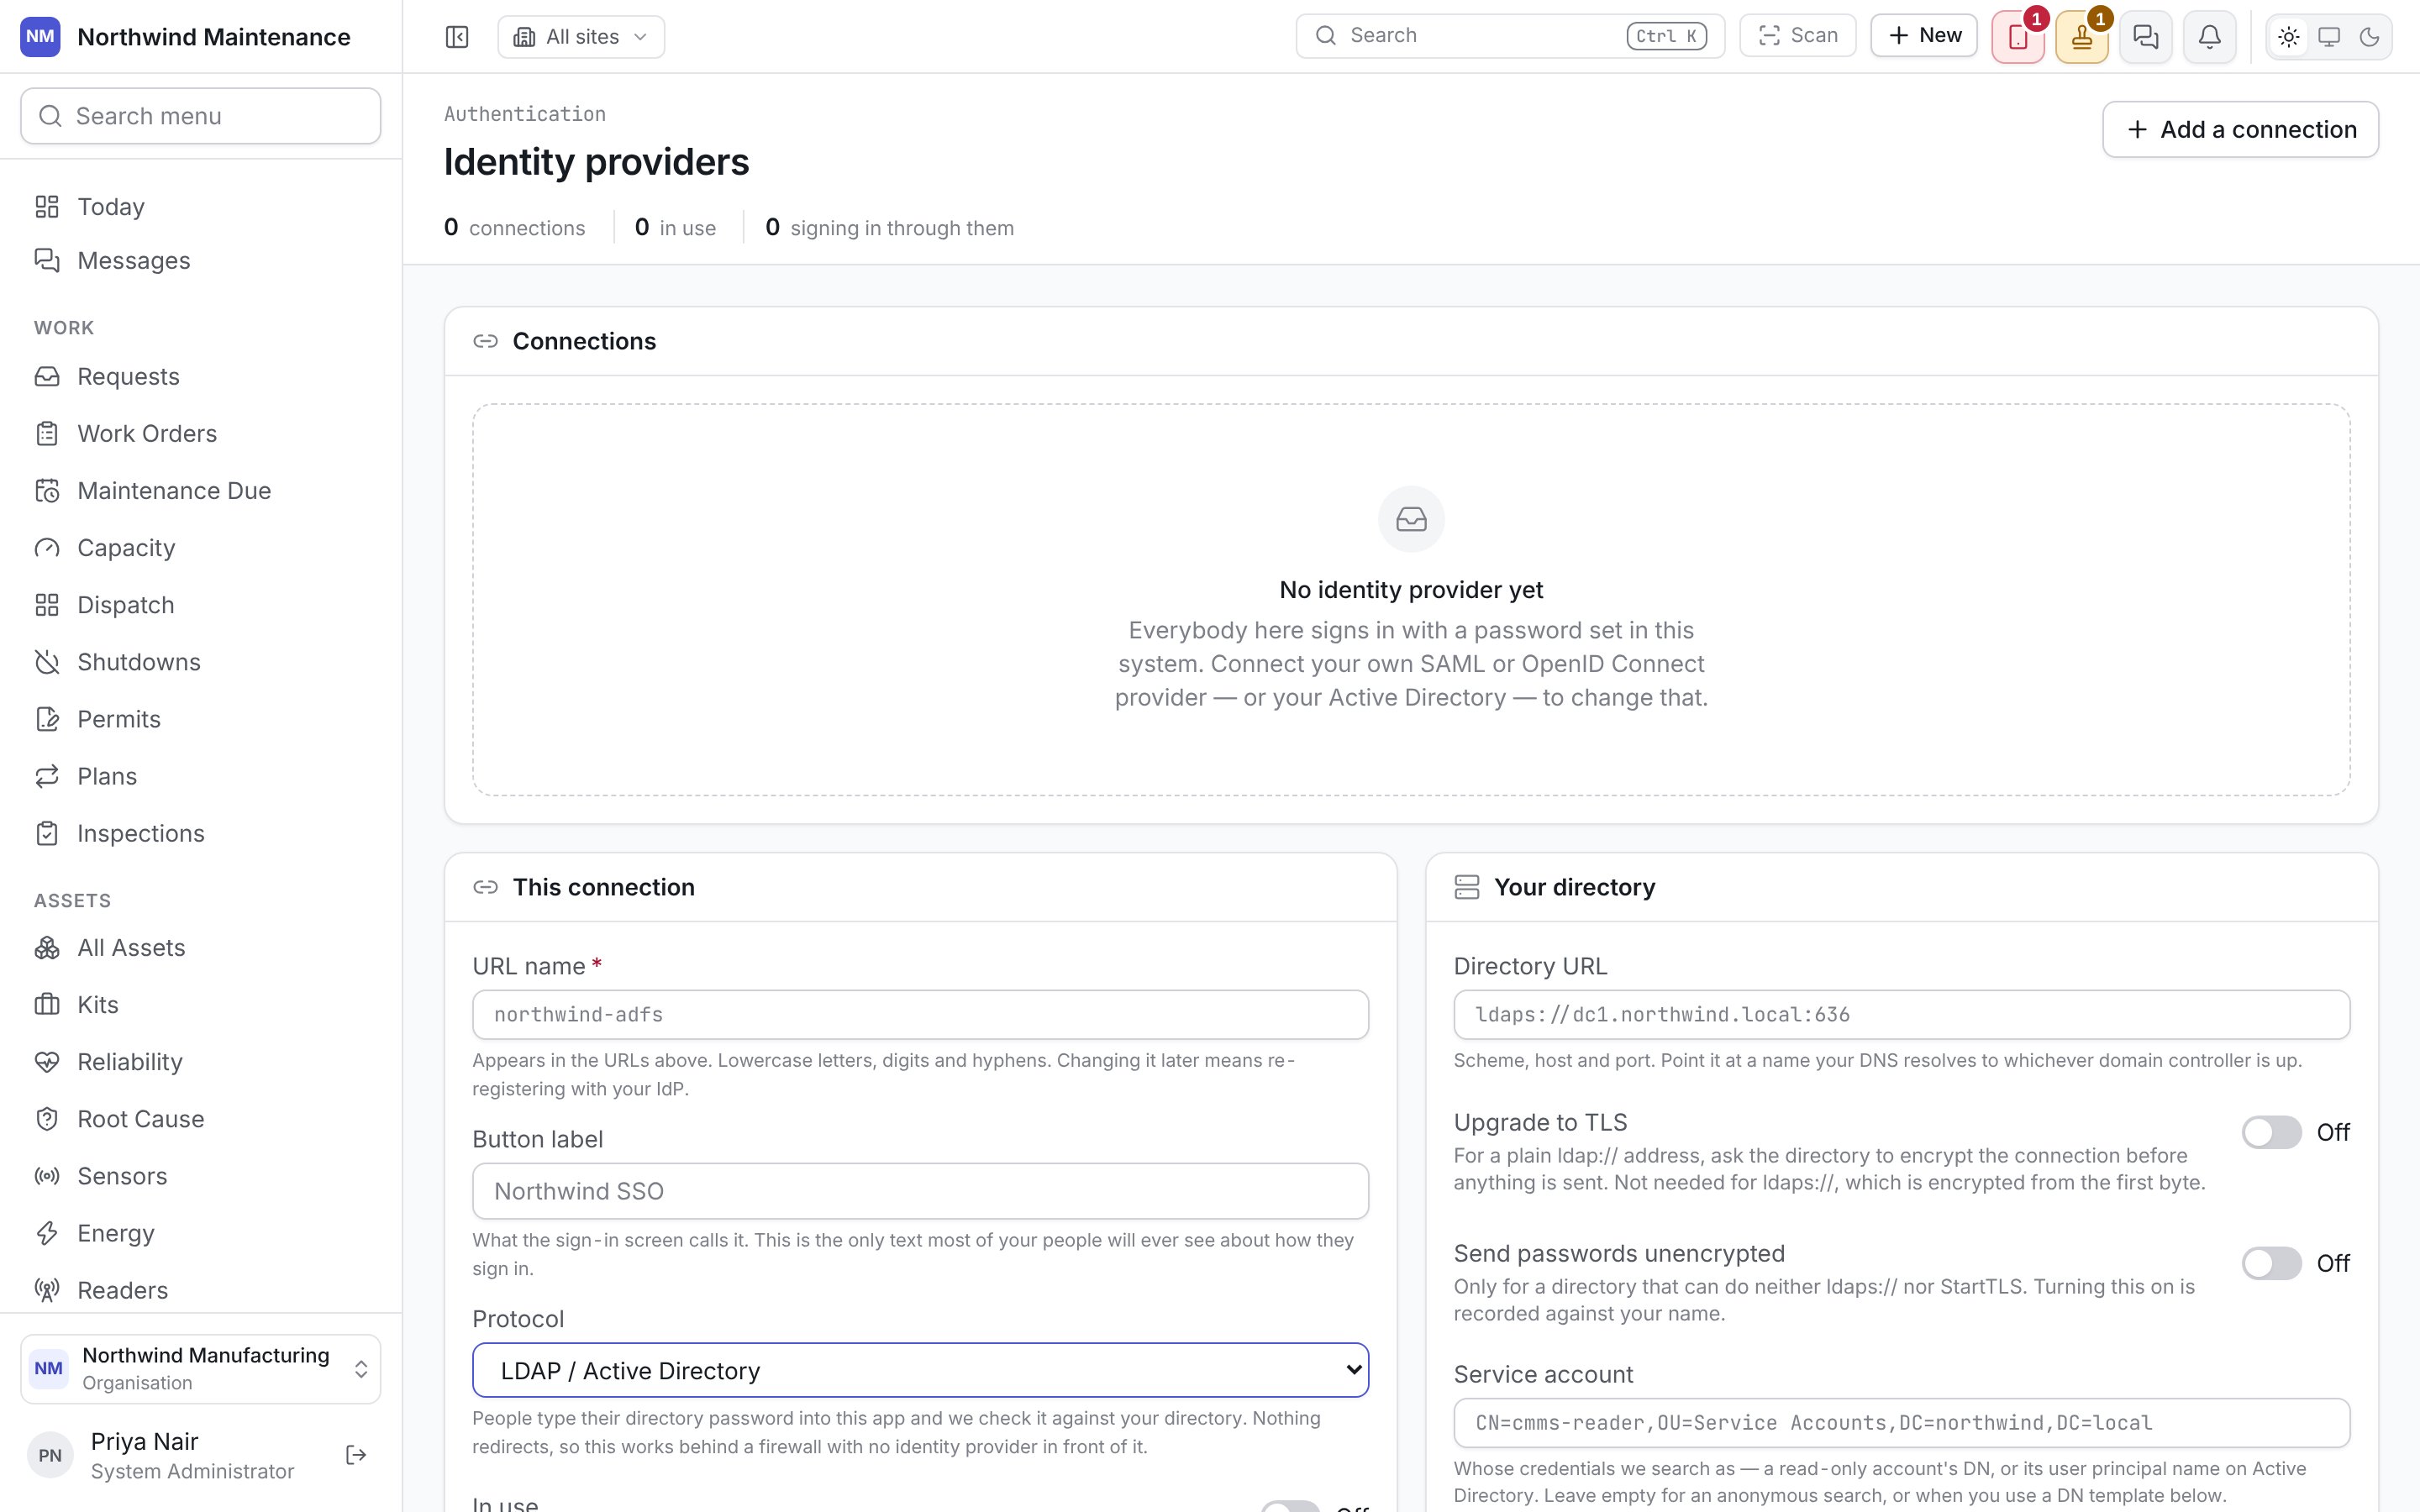
Your directory
Whether it works
An LDAP connection has no console of its own to test from, so once it is saved a Whether it works section appears at the top of the panel. Save and test saves the connection first (the test always uses the saved values) and then tries it. It reports each step it got through rather than a bare pass or fail — reached the address, negotiated encryption, the service account was accepted, the search found somebody — with a tick or a cross beside each. It never asks for or checks anybody’s own password. The last line is the verdict: This connection reached your directory. Switch it on when you are ready. or This connection is not working yet. Nobody is being offered it while it is switched off. Editing any field clears the report, because it described the values that were saved when it ran.Windows sign-in
A saved LDAP connection also has a Windows sign-in section. With it set up, people already signed in to Windows on a PC in your domain go straight in when they open the address you name here, with no password. Each time, your directory is asked whether their account is still enabled, and they also need an active account in this organisation. Anybody else sees the usual sign-in screen. Windows sign-in finds people by their Windows account name, so the connection needs a branch to search under (Where people are) rather than a DN template. Without one the section says so and cannot be filled in.
Save Windows sign-in saves this section on its own, separately from the rest of the connection.
This screen cannot tell whether the keytab is right, so run Save and test under
Whether it works afterwards and then open the address on a domain PC.
People added with Add from your directory are
linked to their directory entry, which is what Windows sign-in matches first.
Reading the assertion or the entry
These fields say where in the assertion (SAML and OpenID Connect) or the directory entry (LDAP) the person’s details are found. Leave them empty and the usual places are tried: the NameID and the standard SAML and OpenID Connect claims, or for LDAPmail, givenName, sn and memberOf.
Who gets an account
Whether a password still works
When passwords are off, a warning reminds you that an outage at your identity provider then stops
everybody signing in except the break-glass role. Test the connection before you save, and make
sure somebody who is around today holds that role.
Signing certificates and certificate authorities
This section appears once a SAML or LDAP connection is saved, and means a different thing for each.
Retire on a row takes that certificate out of use. To add one, paste its base64 block (with or
without the
BEGIN CERTIFICATE lines) into Add a certificate and click Add certificate.
Check the fingerprint against what your identity provider or certificate authority shows before you
rely on it.
Which groups grant which roles
Once a connection is saved, you can map groups in your directory to roles here. Mappings are applied on every sign-in, not only the first, and they take roles away as well as granting them: somebody who moves out of a group in your directory stops holding the role here. Only roles named in a mapping are touched; anything granted by hand on Access is left alone. Search groups and roles finds a mapping by its group or role, and the filter button beside it narrows the list by either column.
With no mappings, everybody arriving through this connection gets the default role and nothing else.
For LDAP, three more settings sit above the table, for directories that record membership on the
group rather than on the person (OpenLDAP’s
groupOfNames and posixGroup). Active Directory needs
none of them.
On LDAP a group can be matched by its name or its whole DN. Use the full DN where two branches hold
groups with the same name.
Directory provisioning
Group mapping covers arrival: somebody signs in and gets the roles their groups say. What it cannot cover is departure — your directory knows somebody has left and this product does not, until they next try to sign in or until somebody remembers to deactivate them. There are two ways to close that gap, and you need only one.Provisioning (SCIM 2.0)
When you issue a token, a panel shows it once: Copy this now — it is not shown again. This
product keeps only a hash and the last six characters, so nothing can read it back. Paste it into
your identity provider, then click I have copied it. If it is lost, revoke it and issue another.
The token list shows:
The bin icon revokes a token. If any token has been refused, a Last refusal: banner shows why.
Once your identity provider has pushed groups, a table lists them with Group (exactly as it
arrived, which is what mappings match on), People (members) and Grants (the roles it grants
here, or Nothing — not mapped). Use it to copy group names into the mapping table.
When your directory disables somebody, their sessions here end and their next request is refused.
Setting provisioning up in your directory gives step-by-step instructions for Microsoft Entra ID
and Okta, with the values to paste, to send to whoever administers your directory. Two things it
calls out: Entra ID provisions only the people and groups assigned to the application, and Okta
ships Deactivate Users switched off — leave it off and nothing happens when somebody leaves.
Reading accounts from a directory
Read accounts from this directory reads your directory on a schedule and creates, updates and deactivates accounts to match it.- On an LDAP connection it binds as the connection’s service account and reads everybody the search matches, under Where people are. Your directory has no way of saying that somebody has left, so anyone the read no longer finds is treated as gone — which is why there is a deactivation limit.
- On a SAML or OpenID Connect connection to Microsoft Entra ID it uses the connection’s own
client ID and secret, which needs your app registration to be granted
User.Read.All. No SCIM licence is needed.
Save schedule saves these. What would this do? runs a dry run: it decides everything and
writes nothing, so you can read the result first. Read it now runs a real read straight away.
Either is queued and usually picked up within a minute; a line under the buttons says when the
directory was last read and when it is next due.
Every read is listed:
Decisions opens one read’s decisions, refusals first, with Person, Decision (Created,
Updated, Reactivated, Deactivated, No change or Refused) and Why:
If a read could not reach the directory at all, The last read failed: shows the reason.
Who can use this
Provisioning sits behind the same permission as the connection itself, because a token that can
create and disable accounts is the same decision as connecting the directory. See
roles.
Ways to sign in
What your people see on the sign-in screen once a connection is in use.
Authentication
Password rules, lockout, session length and who is signed in now.