

You can start with one and move to the other later without a gap.
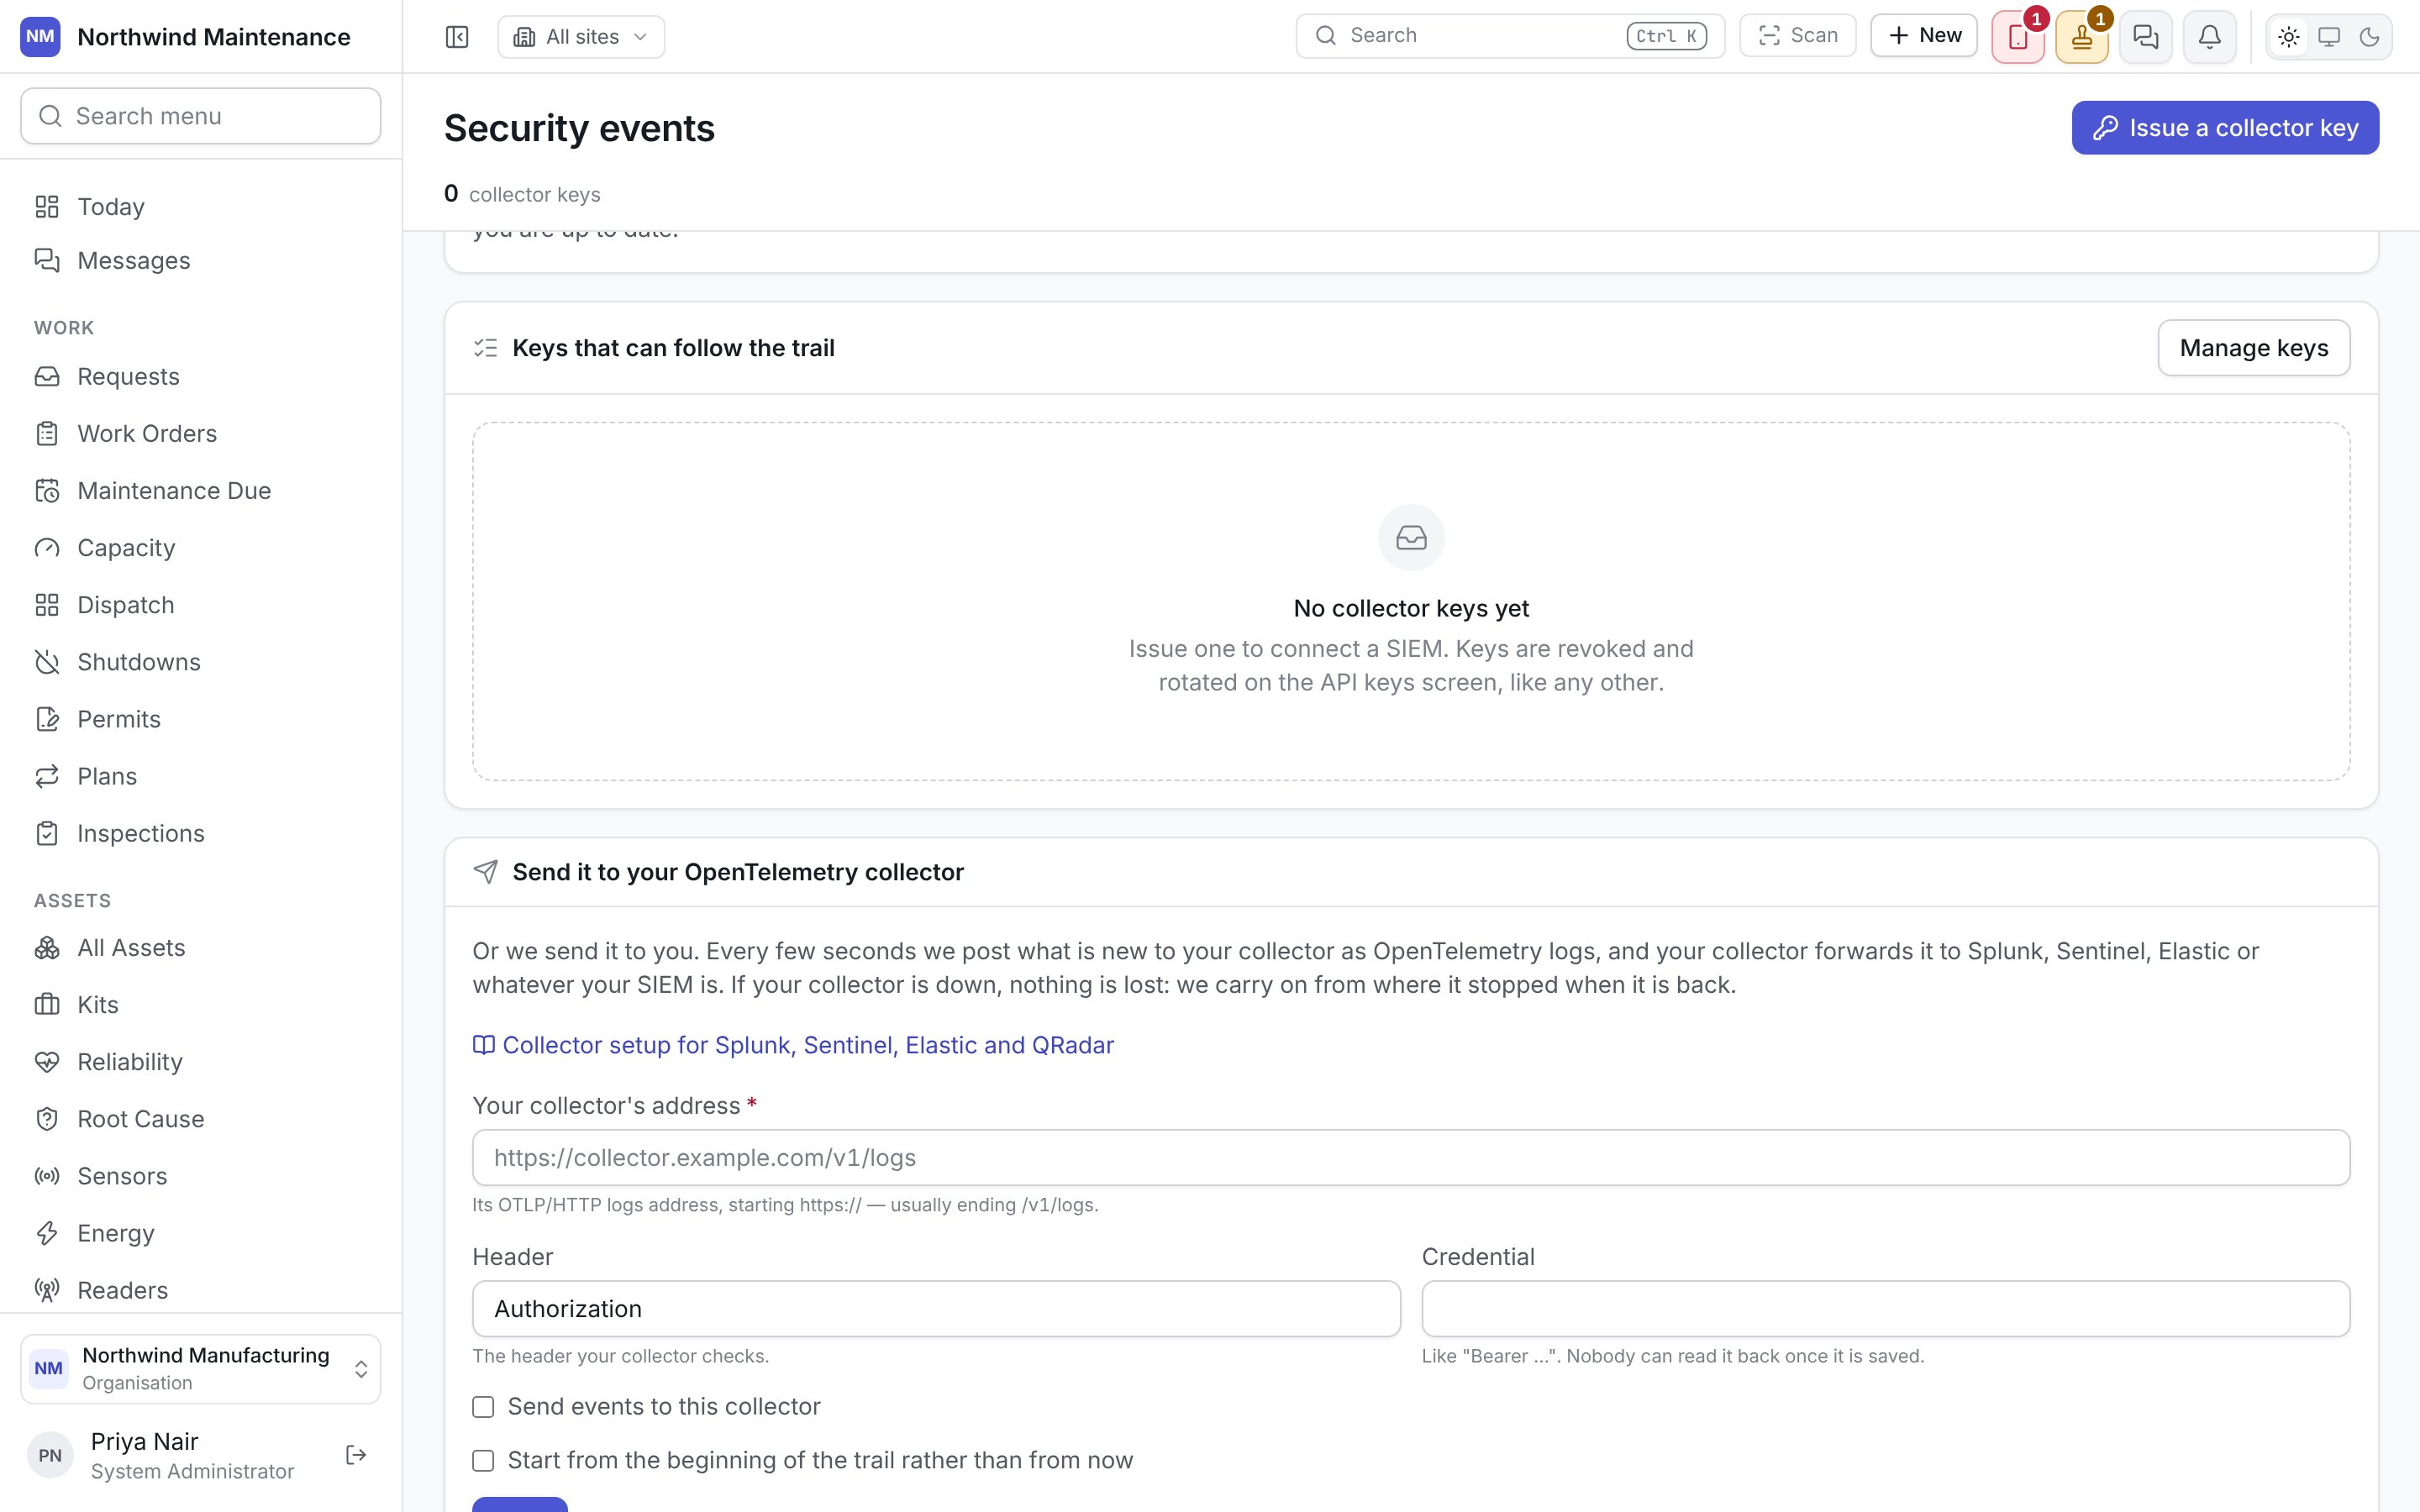
Open it from Administration → Integrations → Security events. The header shows how many
collector keys can currently follow the trail.
What your SIEM receives
The audit trail records two kinds of event. Security events, about getting in:
Changes to data, for every record anybody creates, changes, archives or deletes:
RECORD_CREATED, RECORD_MODIFIED, RECORD_ARCHIVED and RECORD_DELETED.
A person can hold accounts in several organisations with one password. A wrong password is
therefore an attempt on every organisation that password opens. It is recorded in each of them, and
each record names that organisation’s own account. An attempt on an address that nobody holds is not
recorded anywhere, because no organisation owns it.
Each event carries:
Field names leave. Values do not. An event says a work order’s
priority changed, but not
from what to what. The values before and after stay in the product, where reading them is checked
against the person asking. Your SIEM needs to know what happened, and the audit trail keeps the
detail for whoever investigates it.
A link beside the section heading, Every attribute, as your SIEM sees it, opens
what each event carries.
Your SIEM fetches it
Your SIEM signs in with a collector key and asks for everything since the last event it received. Nothing is missed and nothing is sent twice, even if the SIEM was switched off for a week.Issuing a collector key
Click Issue a collector key. This creates three things:- a service account called SIEM collector
- a role of the same name, which can follow the audit trail and do nothing else
- a key for that service account
The requests your SIEM makes
The Connect your SIEM section shows the two requests a collector makes, with this organisation’s address filled in, ready to copy into your SIEM’s HTTP input:- Trade the collector key for a session token. The token is good for fifteen minutes; reuse it for all of them.
- Ask for the events after the last one you stored, sending the token. The answer is a page of events, oldest first.
cursor. Store the cursor of the last event on each page, and send it with the
next request.
A page holds up to 1,000 events. When a page comes back empty, you are up to date. Ask again whenever
you like.
A change that is still being saved when your SIEM asks is held back until it is finished, not
skipped. So the feed can run a few seconds behind the screen, but it never has a gap.
We send it to you
The Send it to your OpenTelemetry collector section sends new events every few seconds to an OpenTelemetry collector, as OTLP logs over HTTPS. The collector then forwards them to your SIEM. Connecting your SIEM has a collector configuration for Splunk, Microsoft Sentinel, Elastic and QRadar.
People without the permission to configure integrations see only Sending to and the address.
Click Save, then Send a test event (offered once the stream is saved). The test posts a single event to your collector, marked
as a test. The result appears under the form: either The last test was accepted, or The last
test was refused with the reason your collector gave. Nothing moves on for a test, so you can send
as many as you need.
Remove the credential deletes the stored credential, for a collector that does not need one.
Changing the address does not restart the stream. A replacement collector picks up where the old one
stopped.
Is it keeping up?
The section header shows Sending, Failing or Off. Below the form:
If your collector is down or refuses a delivery, The last attempt failed, and we will try again
shows the reason. Nothing is lost while it is down. Events wait, the gap between attempts grows up to
an hour, and delivery carries on from the first event your collector does not have.
If your collector accepts a page but turns down particular events in it, those events are counted
and not sent again. A collector that turns an event down because of its content would turn it down
again.
Who can use this
Connecting a SIEM hands it the whole audit trail. So this screen is only for people who may export
that trail themselves. See roles.
Connecting your SIEM
A collector configuration for Splunk, Microsoft Sentinel, Elastic and QRadar.