

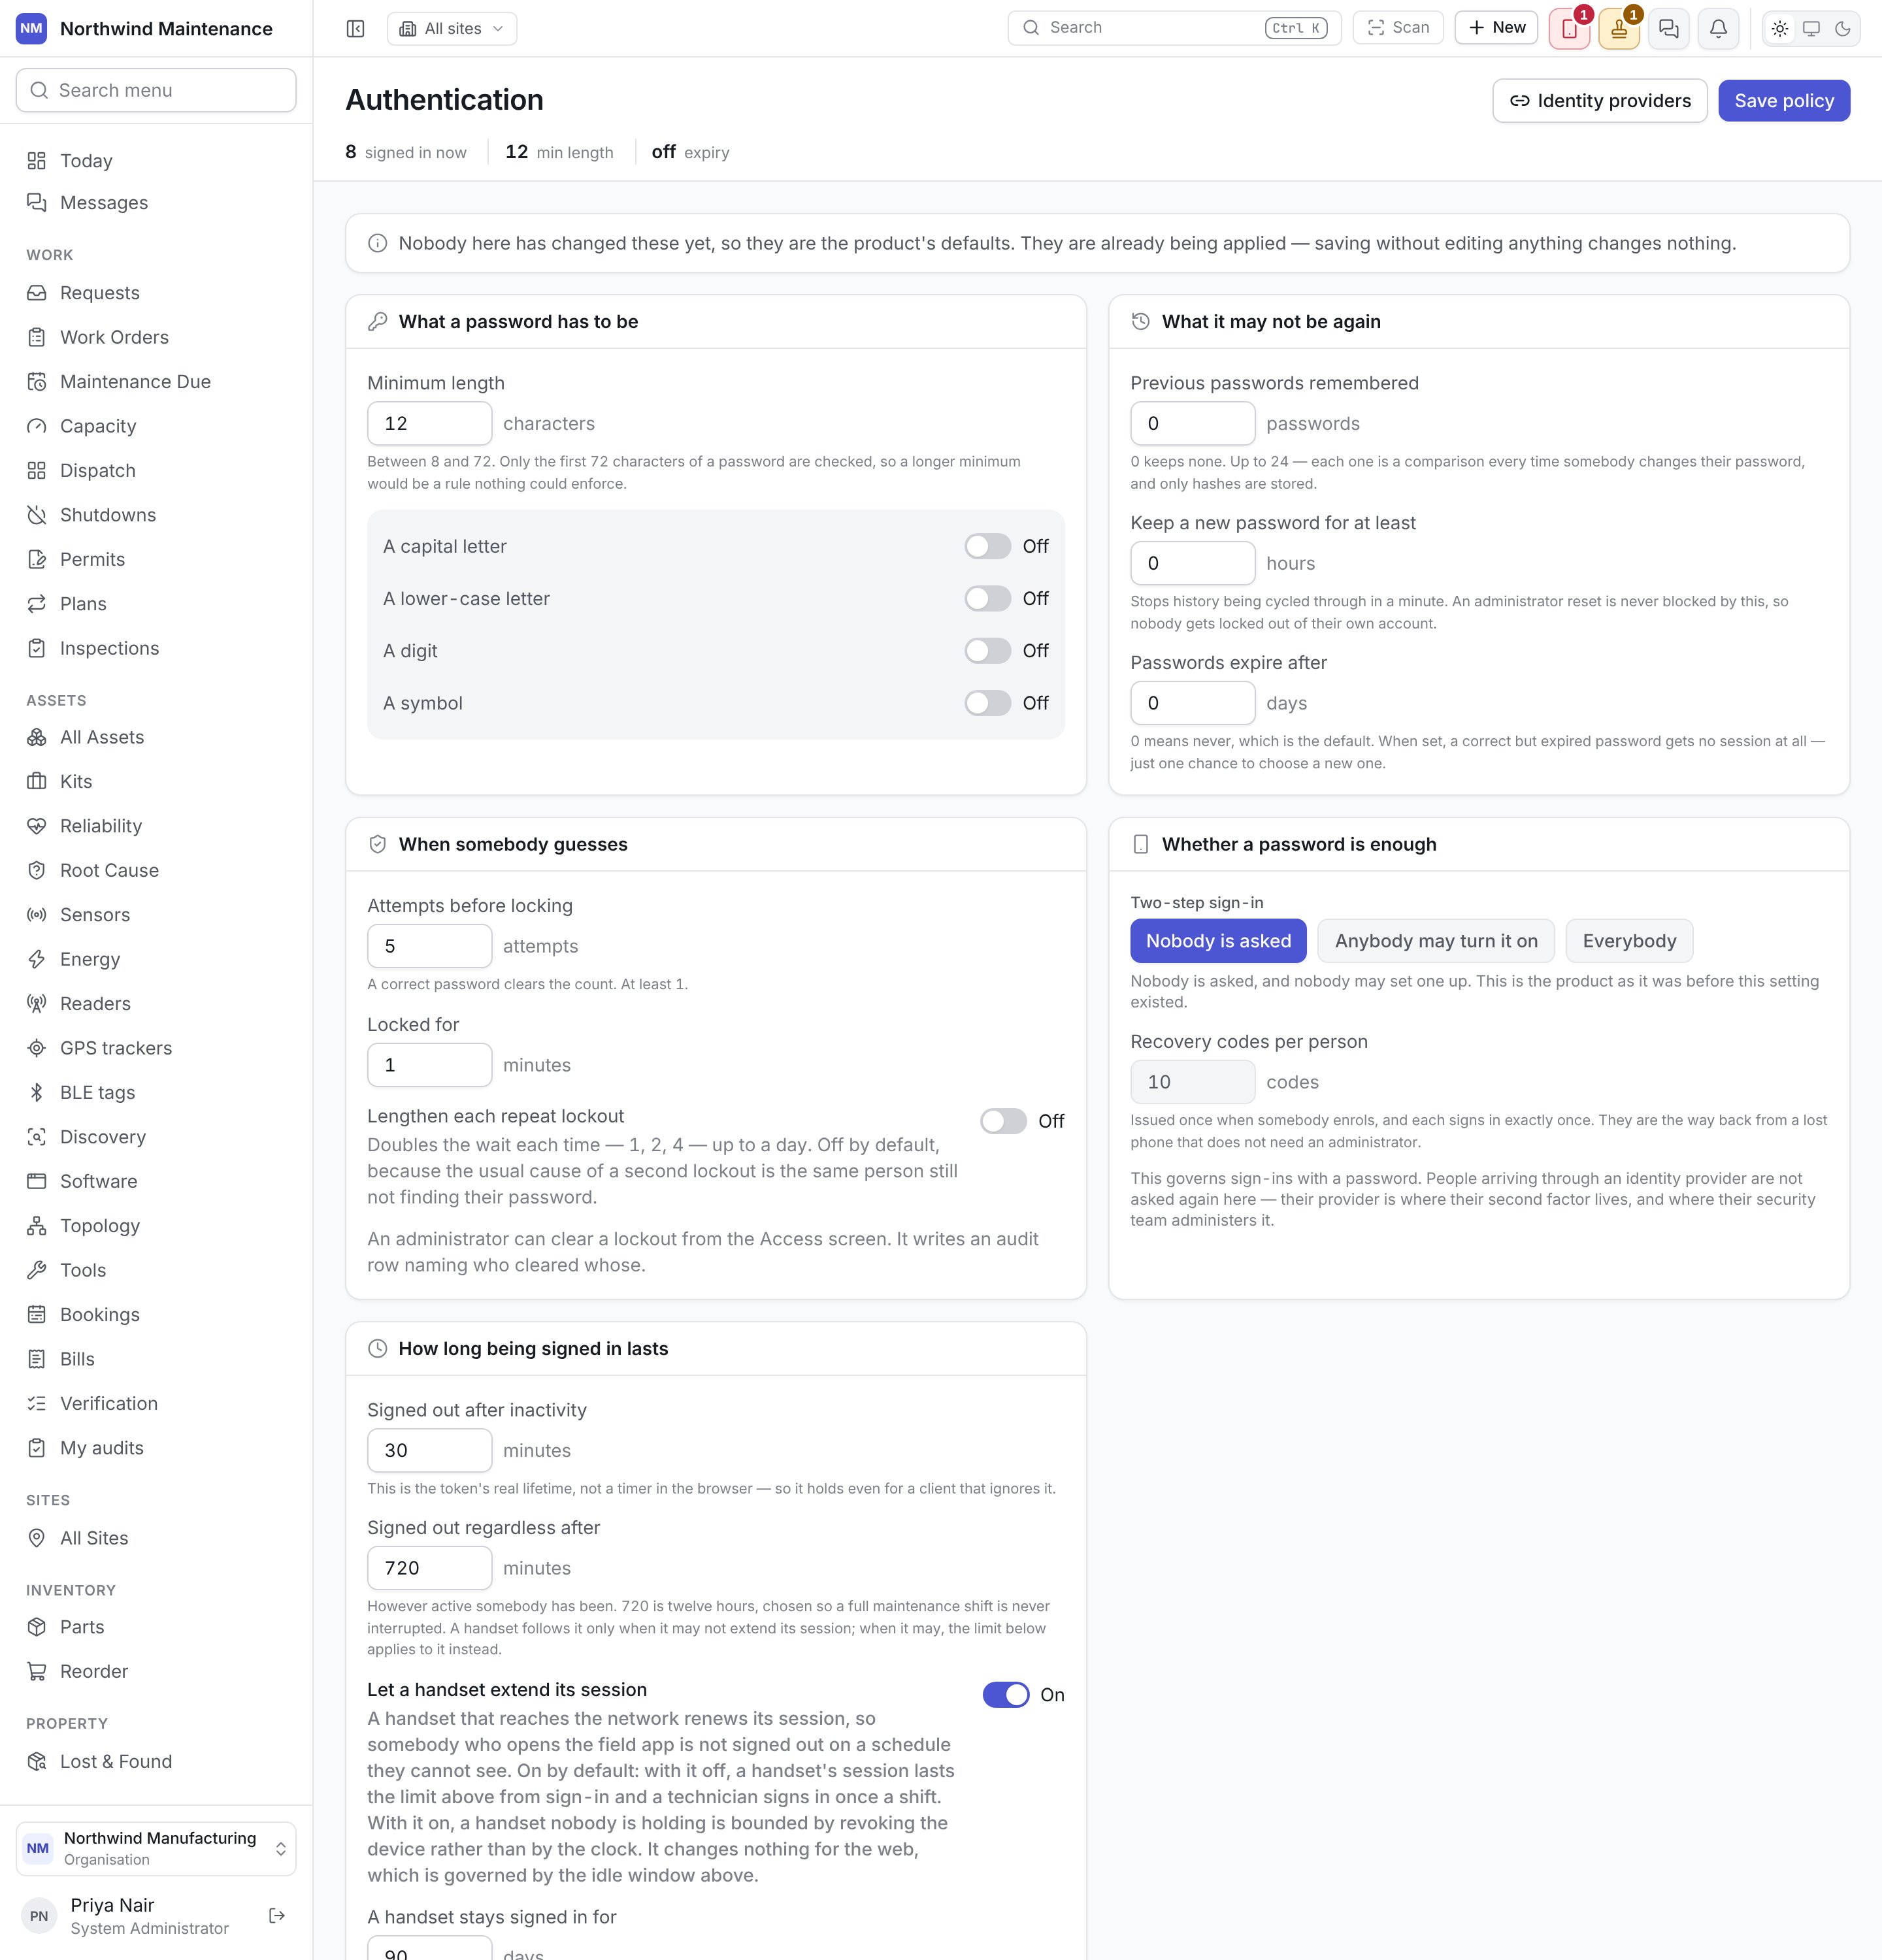
Every rule here is applied by the server on every sign-in and every password change, not by this
screen. An organisation that has never opened it is running on the product’s defaults — the banner
“Nobody here has changed these yet, so they are the product’s defaults” says so, and saving without
editing anything changes nothing.
What a password has to be
What it may not be again
When somebody guesses
An administrator can clear a lockout early from the banner on the Access screen,
which writes an audit entry naming who cleared whose. Resetting a password through the emailed link
also clears any lockout.
Whether a password is enough
Two-step sign-in has three settings:
Enrolling shows a QR code for an authenticator app and the recovery codes, once. An administrator can
see who is enrolled, and clear somebody’s authenticator, from the Two-step sign-in panel on the
Access screen.
Two-step sign-in governs password sign-ins only. People arriving through an identity provider are
not asked again here — their second factor lives with their provider, administered by their own
security team.
How long being signed in lasts
If the inactivity window is set longer than the absolute limit, the screen warns that every session
would end before its first renewal, and saving is refused.
Who is signed in
A register of sessions, newest first, with a count of how many are live out of those shown.
End on a live row ends that session: the next request it makes is refused, not merely its next
renewal. For a lost handset, End each of its sessions here; if the handset must not be able to
sign in again, suspend the account as well. The device itself is revoked
by the person it is enrolled to, from Your devices → I no longer have this on their
profile. That ends its access at once and asks it to destroy the
copy of their work it holds — anything it had queued and not sent is lost. Signing out of the field
app ends that handset’s sessions in every organisation it holds.
Who can use this screen
Somebody who can open the screen but not change the policy sees the values read-only, with a note
saying so. See the permission reference.